An external network location is a host or URL outside Snowflake that a data pipeline may contact. Snowflake controls access through an external access integration rather than exposing credentials directly in the pipeline. section 7.1
Configure access in three stages:
- Create an egress network rule representing one or more external hosts. section 7.1
- Create a secret containing the API token, key, or password instead of embedding the credential value. section 7.1
- Create an enabled external access integration that includes the network rule and permitted secret, then grant users access to the integration. section 7.1
Calling Yelp
A pipeline can represent api.yelp.com with a HOST_PORT egress network rule, protect the Yelp API token in a generic-string secret, and attach both objects to YELP_API_INTEGRATION before retrieving customer reviews. section 7.1
Figure 7.1 Snowflake's external network access architecture consists of a network rule pointing to an external network location and a secret containing a token, key, or password. The network rule and secret are included as parameters when creating an external access integration object. This object is passed as a parameter to a Python function or stored procedure so that the function or procedure can call the external API.
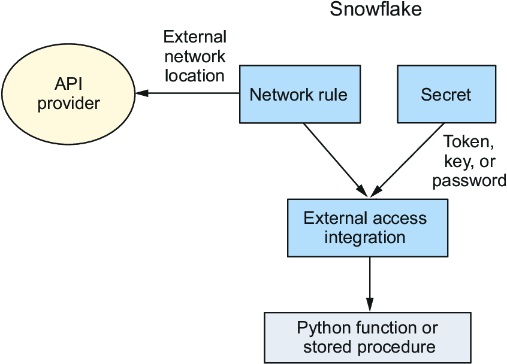
Shows how the network rule and secret become parameters of an external access integration, which a Python function or stored procedure uses to call an external API. section 7.1
