A network rule specifies permitted external network locations together with the direction and type of traffic. In an external-access pipeline, it provides the location boundary that an external access integration allows a stored procedure or UDF to reach. section 7.1 section 7.5
Configure the rule as one component of controlled external API access:
- Choose the external API host and represent it with a network rule. section 7.1
- Set the traffic mode and location type; the demonstrated rule uses EGRESS and HOST_PORT. section 7.1
- Combine the rule with a secret in an external access integration, then pass that integration to the function or procedure. section 7.1 section 7.5
Allow the Yelp API host
use role SYSADMIN; create network rule YELP_API_NETWORK_RULE mode = EGRESS type = HOST_PORT value_list = ('api.yelp.com'); section 7.1
Figure 7.1 Snowflake's external network access architecture consists of a network rule pointing to an external network location and a secret containing a token, key, or password. The network rule and secret are included as parameters when creating an external access integration object. This object is passed as a parameter to a Python function or stored procedure so that the function or procedure can call the external API.
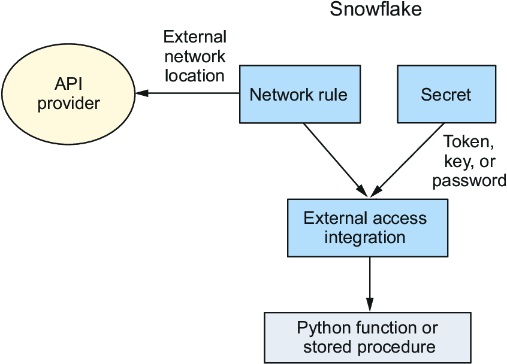
Trace how the network rule points to an external location, joins a credential secret, and becomes part of an external access integration. section 7.1
