Google Cloud IAM governs access to Google Cloud resources through granular permissions. For connected clusters, project-level IAM remains necessary even when cluster-level authorization is configured. section 2.8 section 2.3.2
Operationally, IAM establishes access boundaries around connected-cluster workflows:
- Require permission to view the Google Cloud project before allowing Google Cloud console or Connect functionality. section 2.3.2
- Use separate permissions to grant direct cluster access without granting remote access through Google Cloud. section 2.3.2
- Combine IAM with role-based access control, which allows or denies access to requested resources. section 2.8
- Review Access Transparency controls and logs when Google personnel access customer content. section 2.3.2 section 2.8
Layered request authorization
A request from the Anthos UI travels through a persistent Connect Agent tunnel, with each stage authenticating the request identity and rejecting unauthorized transitions. section 2.3.2
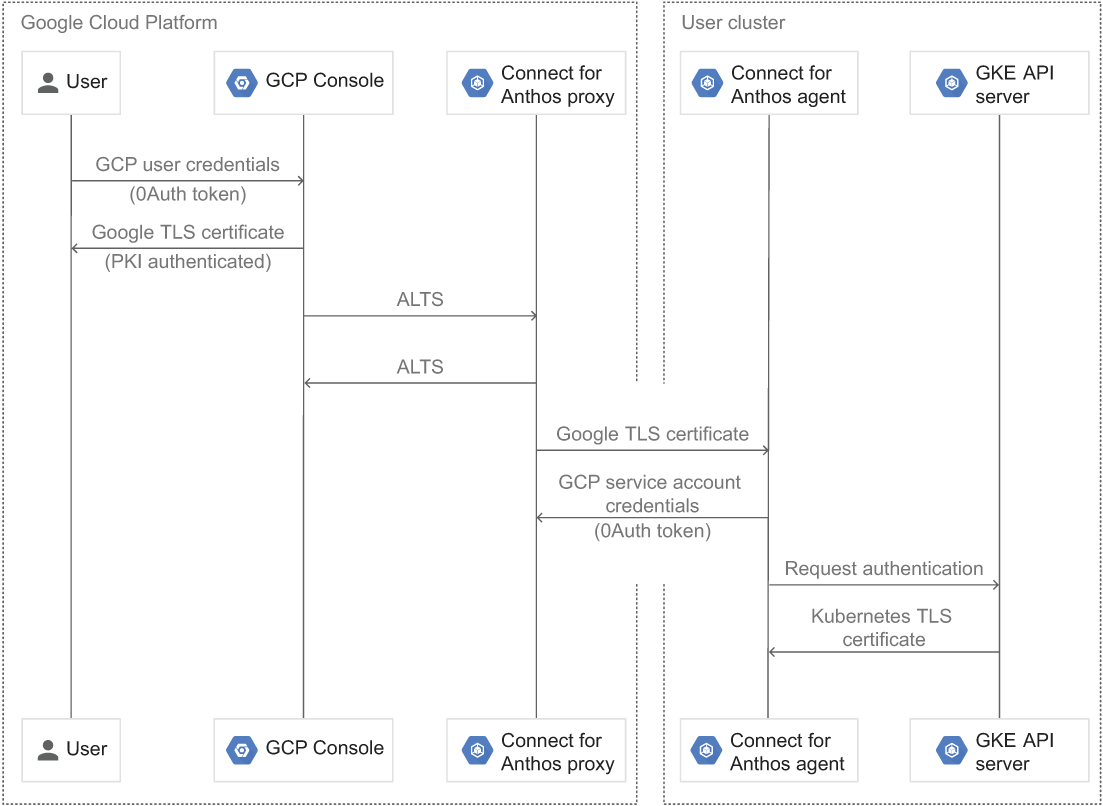
Trace the request-validation stages between Google Cloud and the cluster. section 2.3.2
