HITRUST is a proprietary, prescriptive cybersecurity framework and certification. It defines detailed controls, implementation requirements, measurements, management practices, and assessment procedures for achieving a validated score. section 1.5.1
HITRUST organizes cybersecurity expectations into:
- 19 domains containing controls selected according to an organization’s environment and risk profile. section 1.5.1
- Illustrative procedures evaluated through policy, procedure, implementation, measurement, and management expectations. section 1.5.1
- A validated assessment that determines whether the organization reaches the required certification score. section 1.5.1
Certification assessment
An organization pursuing HITRUST certification maps its environment and risk profile to applicable domains, follows prescribed procedures, measures implementation, and undergoes a validated assessment against the required score. section 1.5.1
Figure 1.2 HITRUST scoring criterion by percentage. The percentages indicate the weights placed on each category for scoring purposes.
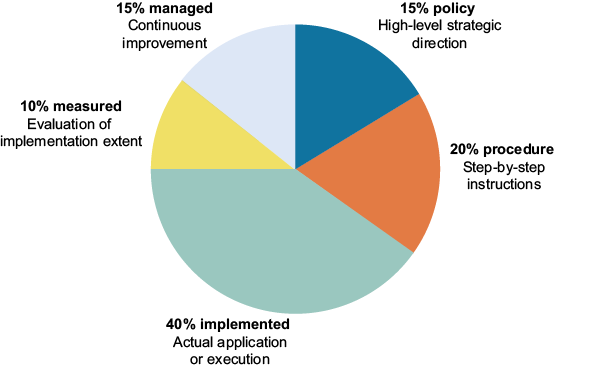
Use the scoring visual to inspect how HITRUST assigns percentage weights across assessment categories. section 1.5.1
