A prescriptive framework specifies detailed steps, controls, measurements, policies, and practices for achieving and maintaining a defined cybersecurity state. By reducing ambiguity, it supports consistent implementation and compliance across organizations. section 1.5.1
HITRUST applies prescription through:
- Controls whose implementation, measurement, and management are explicitly specified. section 1.5.1
- Nineteen domains whose controls reflect organizational environment and risk profile. section 1.5.1
- A validated assessment that scores adherence to prescribed controls and practices. section 1.5.1
HITRUST certification
An organization seeking HITRUST certification follows the framework’s detailed procedures and illustrative controls, then demonstrates sufficient adherence through a validated assessment score. section 1.5.1
Figure 1.2 HITRUST scoring criterion by percentage. The percentages indicate the weights placed on each category for scoring purposes.
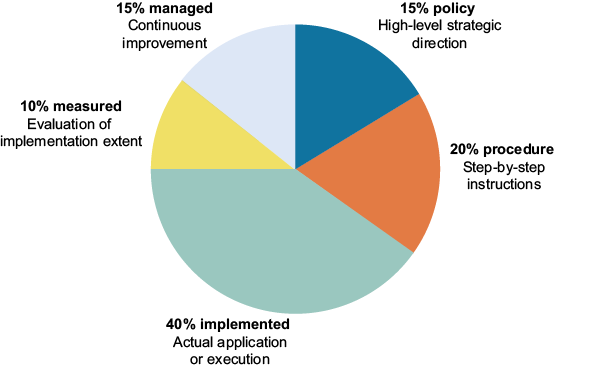
Use the scoring criterion to interpret how percentage weights contribute to HITRUST assessment results. section 1.5.1
