The HTTP Authorization header carries credentials for authenticating an HTTP request. With Spring Security's default HTTP Basic access authentication, its value begins with Basic and continues with the Base64 encoding of username:password. section 2.2
A practical Spring Security request follows this sequence:
- Omit the header and the protected endpoint responds with HTTP 401 Unauthorized. section 2.1
- Supply valid credentials and the request reaches the endpoint, producing HTTP 200 and its response body. section 2.1
- Treat Base64 as encoding rather than encryption or hashing; use HTTPS to protect credentials in transit. section 2.2
Calling a protected endpoint
curl -H "Authorization: Basic dXNlcjo5M2EwMWNmMC03OTRiLTRiOTgtODZlZi01NDg2MGYzNmY3ZjM=" http://localhost:8080/hello returns Hello! The same credentials can be supplied with curl's -u option. section 2.1
Figure 2.1 Our initial application employs HTTP Basic for user authentication and authorization when accessing an endpoint. It offers a REST endpoint at a specified route (/hello). Upon a successful request, it issues an HTTP 200 status message along with a response body. This instance illustrates the default authentication and authorization mechanisms set up by Spring Security.
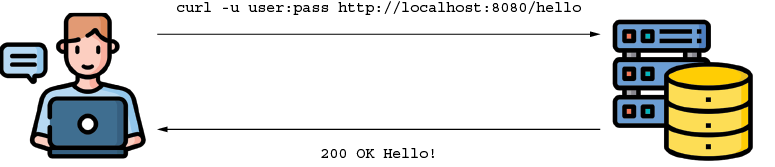
Trace the default Spring Security flow from an HTTP Basic request to authentication, authorization, and the protected REST response. section 2.1

