An Azure tenant represents an organization in Azure. It provides a dedicated directory for identity information about users, groups, and applications, and it performs identity and access management functions for tenant resources. section 2.1.1
A tenant is created when an Azure subscription is created. One Microsoft Entra ID directory can be associated with many subscriptions, while each subscription is associated with only one directory. This lets multiple subscriptions use the same secured identities. section 2.1.1
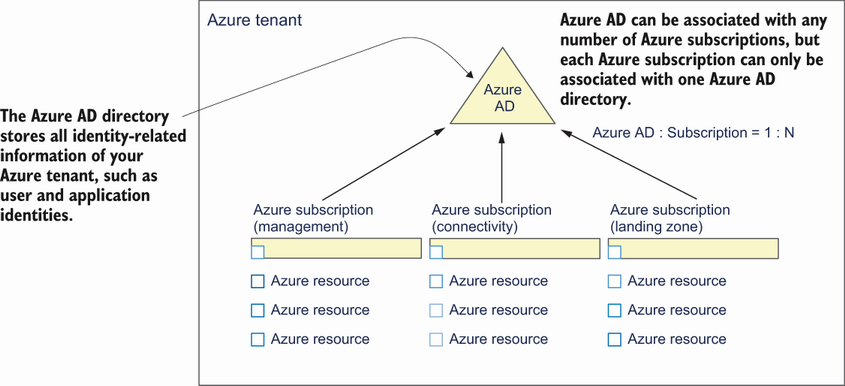
Use the relationship diagram to see how one tenant directory can serve multiple Azure subscriptions. section 2.1.1
The tenant is also a logging boundary. Azure monitoring can collect data from applications, operating systems, compute resources, subscriptions, and tenant-level services such as Microsoft Entra ID. section 9.1
Tenant-level Microsoft Entra ID logs support identity investigation:
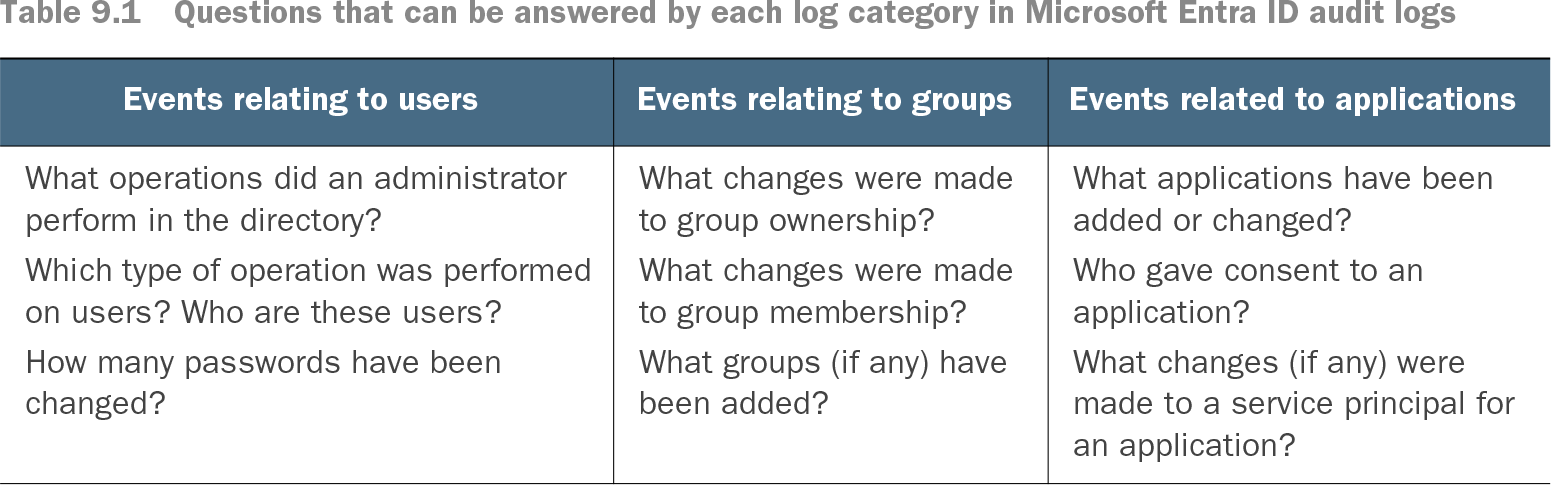
- Audit logs record directory events involving users, groups, and applications, including password resets, group membership changes, application changes, and consent. section 9.1.1
- Sign-in logs classify interactive and noninteractive user sign-ins, service principal sign-ins, and managed identity sign-ins. section 9.1.1
Investigating a suspicious password reset
A password reset can be a legitimate self-service or administrator action, but it can also signal suspicious activity. Audit log records can identify which user’s password changed and who performed the operation; they can also expose attempts to add a compromised user to an administrator group. section 9.1.1
Table 9.1 Questions that can be answered by each log category in Microsoft Entra ID audit logs (view table figure)
Browse the audit-log question categories to map user, group, and application changes to an investigation. section 9.1.1