liveBook · Manning

Microsoft Entra ID audit log

As explained in Azure Security

A Microsoft Entra ID dataset containing records of directory-related operations and administrative activities in an Azure tenant.

The Microsoft Entra ID audit log records directory operations and administrative activity across an Azure tenant. It helps investigate lateral movement and privilege escalation, such as unauthorized password resets or additions to administrator groups. section 9.1.1

Audit records commonly answer questions about:

  • Users: which operations affected users, who performed them, and how many passwords changed. section 9.1.1
  • Groups: changes to ownership, membership, and newly added groups. section 9.1.1
  • Applications: newly added or changed applications, consent grants, and service-principal changes. section 9.1.1
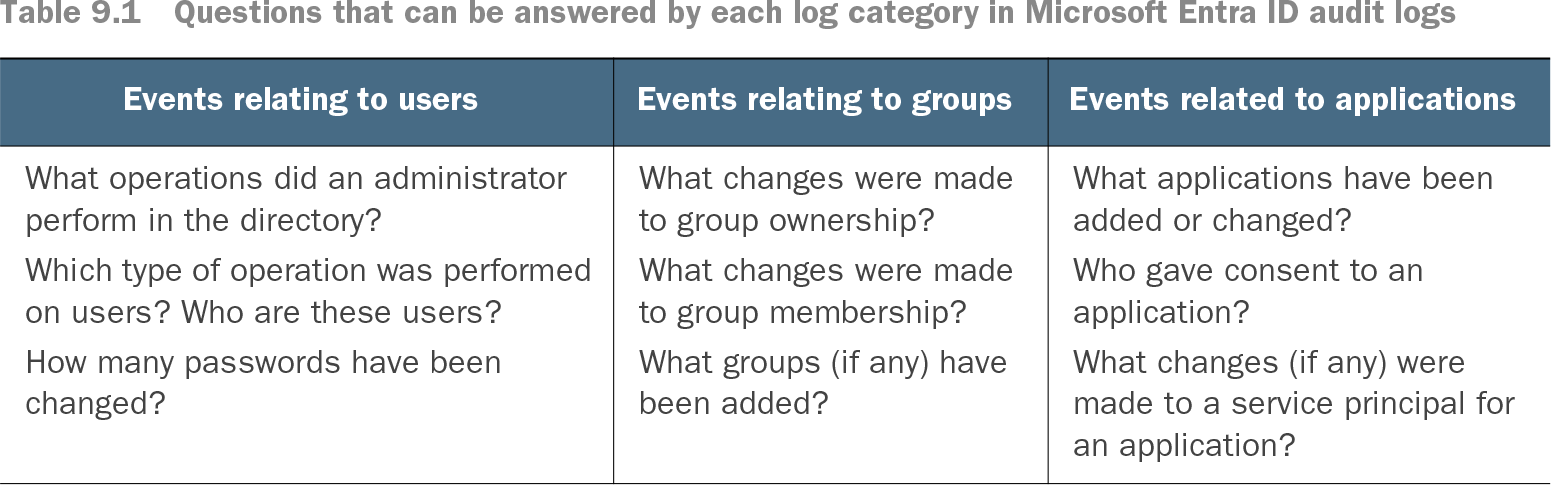
Table 9.1 Questions that can be answered by each log category in Microsoft Entra ID audit logs (view table figure)

Events relating to users

Events relating to groups

Events related to applications

What operations did an administrator perform in the directory?

Which type of operation was performed on users? Who are these users?

How many passwords have been changed?

What changes were made to group ownership?

What changes were made to group membership?

What groups (if any) have been added?

What applications have been added or changed?

Who gave consent to an application?

What changes (if any) were made to a service principal for an application?

Use the question-to-category table to choose the relevant audit-log records during directory investigations. section 9.1.1

How Azure Security covers it

How deep it goes
Explains recorded event categories and investigative questions without detailing log collection commands or query construction.
Examples
Uses password resets, administrator-group additions, group membership changes, application consent, and service-principal modifications.
What it assumes
Assumes familiarity with an Azure tenant and Microsoft Entra ID as the directory service managing users, groups, and applications.
What you can do after
Evaluate/understand directory changes and identify audit records relevant to suspicious identity or administrative activity.
How it connects
Connects Microsoft Entra ID audit logs with Azure Monitor, users, groups, applications, service principals, and sign-in logs.

Related concepts

This explainer was generated by Manning's knowledge graph from the text of Azure Security. The section links point to the parts of the book it draws on.