A network namespace is a Linux isolation boundary that gives processes a separate view of network devices and configuration. It removes access to the host network while providing virtual network devices, helping containers operate as if they had distinct networking. section 1.2 section 10.5
Podman configures networking inside the namespace before starting the container process. Rootful containers use CNI plugins to configure networking devices; rootless containers cannot create devices or modify firewall rules, so slirp4netns provides user-mode networking through a TAP device and relays connections to the host. section 6.2.2 section 6.2.3
Isolating containers with Podman networks
Create private networks with podman network create net1 and net2, then start a container with --network net1. Another container on net1 can resolve and ping it by name, while containers in the default namespace or on net2 cannot. Use --net=host when a container must bind directly to host ports, accepting less network isolation. section 10.5
Figure 6.6 Podman creates a network namespace and launches slirp4netns to relay network connections.
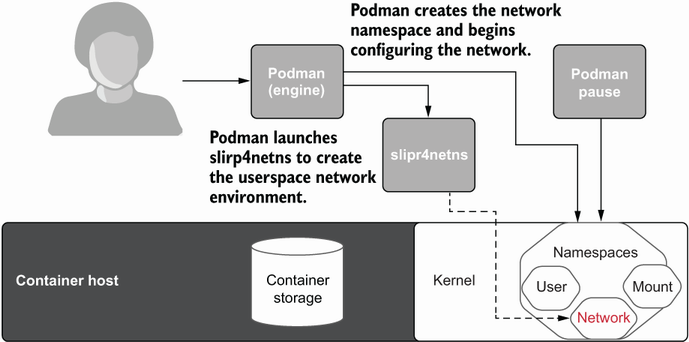
Shows Podman creating a network namespace and launching slirp4netns to relay connections for rootless networking. section 6.2.3

