OAuth 2.0 is an industry-standard authorization framework for delegating controlled access to protected REST API resources. A third-party application acts on a user’s behalf without receiving the user’s credentials. section 23.3.2 section 23.4
The basic authorization sequence is:
- The client application requests authorization from the resource owner. section 23.4
- The client receives an authorization grant and exchanges it with the authorization server for an access token. section 23.4
- The client presents the access token to the resource server to retrieve the desired protected resource. section 23.3.2 section 23.4
Figure 23.7 The basic OAuth 2.0 process. Through access delegation, the client application is able to access the resource owner’s protected resources on behalf of the owner.
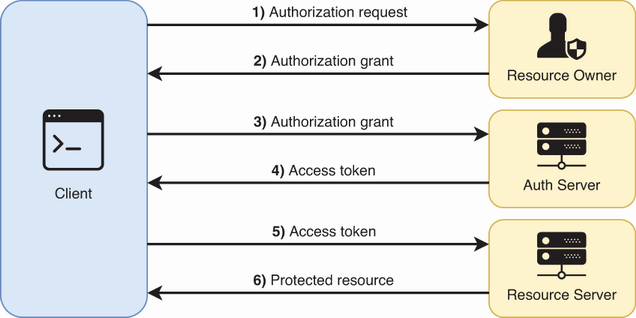
Follow the process diagram to distinguish the resource owner, client application, authorization server, access token, and resource server. section 23.3.2








