The principle of least privilege gives each user access only to resources they own or are authorized to inspect or manipulate. In API security, it limits the damage caused by stolen credentials, excessive roles, or misleading claims by refusing to trust users automatically—even authenticated or supposedly administrative users. section 3.2
Apply the principle through focused API controls:
- Deny access by default, then grant only the operations and resources required for the request. section 3.2
- Protect every endpoint, including internal APIs, and avoid exposing unnecessary operations. section 3.2
- Validate authentication and authorization credentials, and adjust permissions dynamically when conditions change. section 3.2
- Monitor activity and restrict compromised resources to limit continuing access. section 3.2
Catalog access
An unauthenticated e-commerce user may browse the product catalog but cannot upload products or modify product details. section 3.2
Figure 3.10 On an e-commerce platform, an unauthenticated user can browse the catalog but can’t upload new products or change their details.
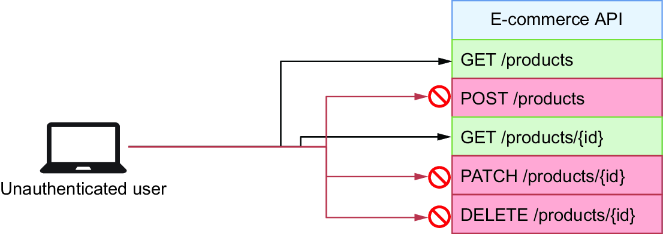
Use the access contrast to check whether each endpoint grants only the operations appropriate to the caller. section 3.2
















