A generative AI model may leak sensitive information even when conventional user permissions are respected. Probabilistic risk management addresses such uncertain outcomes without assuming that controls will behave deterministically. section 1.3 section 1.3
Put the principle into operation by combining established governance with adaptive practices:
- Retain policies, accountability chains, executive oversight, and existing IT and API controls. section 1.3
- Monitor and stress-test continuously, adapting governance as model behavior changes rather than relying on point-in-time audits. section 1.3
- Document model limitations and log inputs and outputs to support transparency. section 1.3
Sensitive information in generated output
Access controls may restrict a user’s permissions while a model still generates output that exposes sensitive information. Governance must therefore consider the output itself, not just whether the user had permission to access a conventional asset. section 1.3
Figure 1.3 Classic GRC compared with AI GRC and GenAI GRC
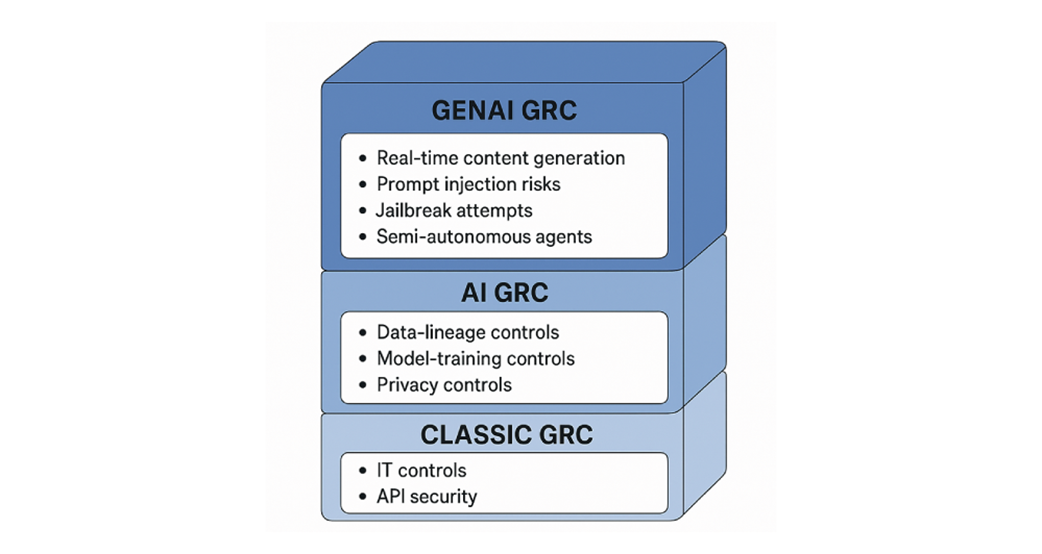
Compare the classic, AI, and generative AI governance layers that adaptive risk management builds on. section 1.3
