Public-key cryptography uses a mathematically related public key and private key. In HTTPS, the browser can see the public key, while only the server holds the private key. section 28.2
HTTPS uses the key pair and certificate chain to protect traffic and establish server trust:
- Data encrypted with the server’s public key can be decrypted only with its private key. section 28.2
- Certificate authorities and trusted root certificates help browsers verify that the certificate belongs to the server. section 28.2
Trusting a development certificate
ASP.NET Core development applications use an HTTPS development certificate. If browsers warn that it is untrusted, trust it with: dotnet dev-certs https --trust. section 28.2
Figure 28.4 The developer certificate is not trusted by default, so apps serving HTTPS traffic using it will be marked as insecure by browsers. Although you can bypass the warnings if necessary, you should instead update the certificate to be trusted.
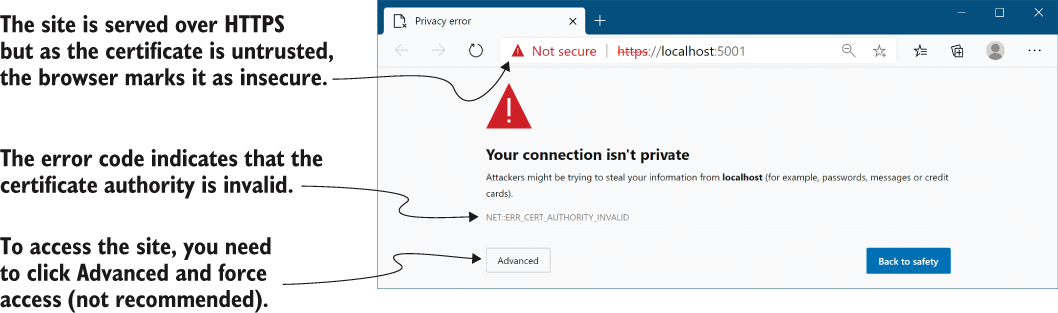
Use the figure to recognize the browser warning produced by an untrusted development certificate. section 28.2




