A public-private key pair is a matching credential set used for asymmetric authentication. AWS can use a key pair to authenticate an administrator logging in to an EC2 Linux machine. section 3.1.1
When launching an EC2 instance, consider these operational properties:
- A configured key pair supports login, but the approach works only for a single user and cannot be changed externally after launch. section 3.1.1
- You can launch without a key pair and use AWS Systems Manager Session Manager, which uses temporary key pairs instead. section 3.1.1 section 3.1.2
- Session Manager avoids requiring inbound SSH or RDP connectivity, reducing the instance’s attack surface. section 3.1.2
Launching an EC2 instance without a key pair
During the EC2 launch wizard, select Proceed without a Key Pair, deselect Allow SSH Traffic, attach an IAM role for Systems Manager, and connect later through the Session Manager tab. section 3.1.1 section 3.1.2
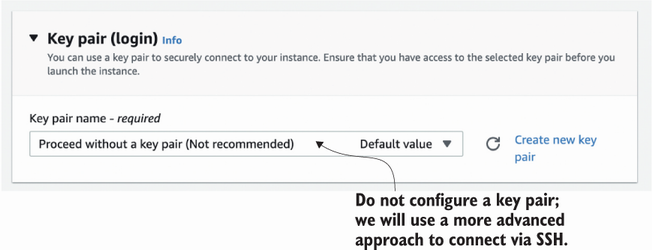
Use the launch-wizard figure to locate the option for proceeding without a key pair. section 3.1.1





