A public subnet is a cloud network segment with internet access. It belongs to a larger segmented topology in which different subnets provide different degrees of access. section 9.2
Internet exposure changes an API’s threat model. Use public subnets as an entry boundary for hardened components such as API gateways, reverse proxies, load balancers, or WAFs, rather than placing application services directly there. Keep internal services in private subnets and connect segments only through deliberate network bridges. section 9.2
Figure 9.10 The DMZ is a region of our network that is exposed to the internet. It’s good practice to channel inbound traffic through the DMZ and keep all our services in private subnets. The DMZ can include elements such as an API gateway and bastion server.
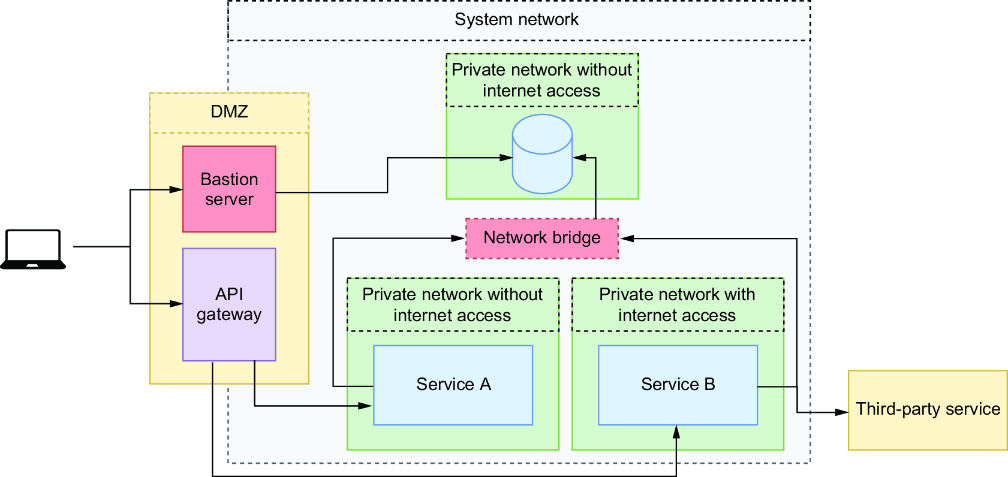
A DMZ illustrates the boundary role of an internet-exposed network region: channel inbound traffic through an API gateway or bastion server while keeping services in private subnets. section 9.2

