PyRIT is an open-source framework for automating red teaming of generative artificial-intelligence systems. It applies known jailbreak and prompt-mutation strategies to produce large numbers of adversarial inputs, helping testers find unsafe behavior before deployment. section 5.9 section 10.22
PyRIT supports adversarial testing while leaving important limitations:
- Scales attacks from human-designed techniques to thousands or even millions of test inputs. section 5.9
- Tests strategies such as prompt injection, adversarial formatting, hypothetical scenarios, and gradual transitions toward unsafe requests. section 5.9 section 10.22
- Complements rather than replaces human testers, who often provide more creativity in complex or multistep conversations. section 5.9
- Produces signals for safety workflows, including prompt changes, dataset updates, tool restrictions, and architectural isolation. section 10.22
From jailbreak idea to scaled test
A tester might begin with a fictional-persona request, a hypothetical scenario, or a gradual conversational shift that previously elicited an unsafe response. PyRIT can then apply related techniques across many inputs, while human testers assess unusual mult turns and production-specific behavior. section 5.9 section 10.22
Figure 5.11 The red-teaming process for LLMs
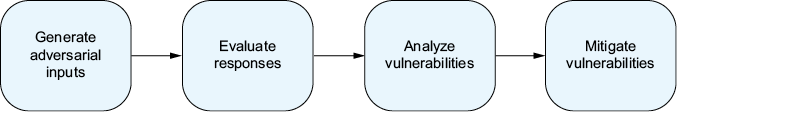
Use the red-teaming process diagram to situate PyRIT within the broader cycle of adversarial testing and defense improvement. section 5.9
