Certificate revocation lets a certificate authority declare an issued certificate invalid before its scheduled expiration, limiting the damage from a compromised certificate. section 9.3 section 9.6
Web systems have used three main approaches:
- Certificate Revocation Lists (CRLs) publish revoked certificates, but can become large and require frequent checking. section 9.3
- Online Certificate Status Protocol (OCSP) provides a web interface for checking whether a certificate is revoked, but depends on highly available CA services and can reveal traffic information. section 9.3
- OCSP stapling lets the website obtain a signed status response and attach it to the certificate during the TLS handshake. section 9.3
Figure 9.9 Certificate revocation on the web has had three popular solutions: Certificate Revocation Lists (CRLs), Online Certificate Status Protocol (OCSP), and OCSP stapling.
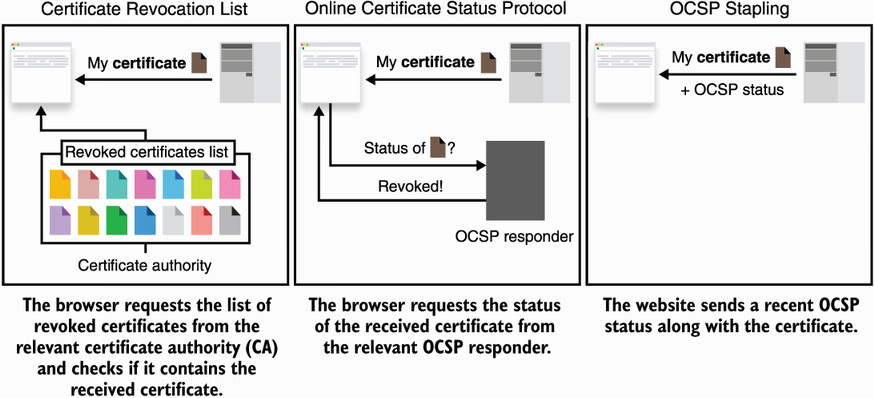
Compare the three revocation paths: published lists, direct status queries, and stapled status responses. section 9.3



