Risk mitigation velocity (RMV) measures the elapsed time from identifying a cybersecurity risk to resolving it. Lower RMV means faster mitigation, less exposure, and fewer opportunities for attackers to exploit vulnerabilities. section 10.7.1
Calculate RMV by tracking resolution time for identified risks and averaging those durations across comparable vulnerabilities or incidents. Compare results by risk type and over time to assess whether the security response is becoming more effective. section 10.7.1
DataSafe vulnerability example
DataSafe resolves a critical vulnerability in 2 days, a moderate vulnerability in 3 days, and a low-risk vulnerability in 6 days. Its average RMV is (2 + 3 + 6) ÷ 3 = 3.67 days. Reducing this average over time lowers exposure to cyberthreats. section 10.7.1
FinSecure improvement target
FinSecure reduces RMV from 15 hours to 9 hours against a target of 10 hours or less by automating response workflows and training its incident-response team. The improvement helps mitigate risks before escalation. section 10.7.3
Figure 10.6 The left side shows the continuous improvement dashboard before the improvements. The right side shows the dashboard after implementation of the improvements.
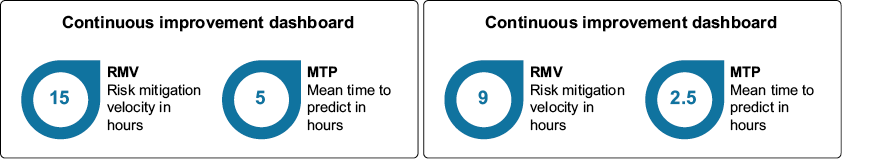
Compare the before-and-after dashboard to see how reduced RMV supports continuous improvement alongside mean time to predict. section 10.7.3
