A role definition is the “what” of Azure role-based access control (RBAC): a named collection of permissions such as read, write, or delete. RBAC combines it with a security principal and a scope to create a role assignment. section 6.7.2 section 6.7
Choose role definitions with maintenance in mind:
- Prefer Azure’s built-in roles, including Owner, Contributor, Reader, DNS Zone Contributor, and other service-specific roles. section 6.7.2
- Create a custom role only when no built-in role fits; custom permissions require ongoing tracking, naming, and maintenance. section 6.7.2 section 6.7.3
- Separate the role definition from scope: the definition states what an identity may do, while scope states where it may do it. section 6.7.3
Assigning Contributor access
For the Alpaca-Ma-Bags identity, open the AlpacaRG resource group, choose Access Control (IAM), select Add Role Assignment, choose the built-in Contributor role, select the members, and review the assignment. Contributor permits management of applicable resources without passing that capability to other users. section 6.7.3
Figure 6.33 RBAC components
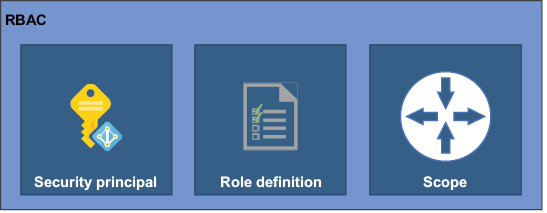
Use the RBAC components diagram to see how the security principal, role definition, and scope combine into authorization. section 6.7

