A root certificate sits at the end of a TLS certificate chain and represents a trusted certificate authority (CA). Browsers trust selected root certificates, allowing them to recognize an HTTPS certificate as trusted. section 28.2
ASP.NET Core development and self-signed certificates lack a root certificate trusted by browsers, so local HTTPS sites show warnings until the certificate is explicitly trusted. Production sites instead need certificates signed by a trusted CA. section 28.2
Trusting the development certificate
On Windows or macOS, run `dotnet dev-certs https --trust` to register the development certificate as trusted and remove browser warnings. section 28.2
Figure 28.4 The developer certificate is not trusted by default, so apps serving HTTPS traffic using it will be marked as insecure by browsers. Although you can bypass the warnings if necessary, you should instead update the certificate to be trusted.
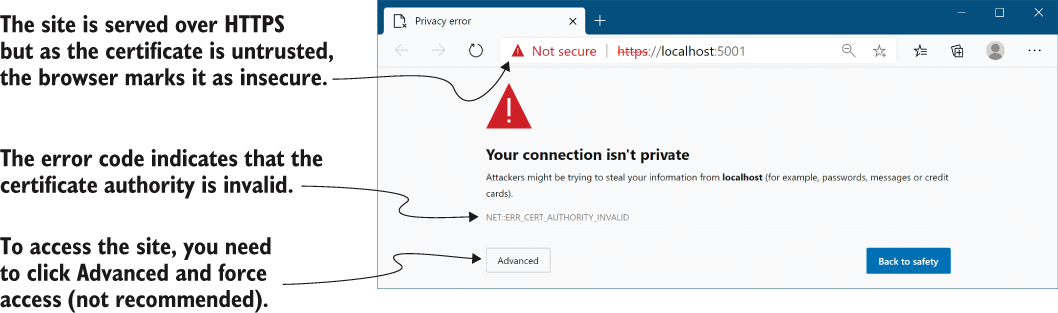
Use the figures to compare browser warnings before and after trusting a development certificate. section 28.2


