PKCS #1 v1.5 protects RSA signatures by requiring a rigid, recognizable encoding before the RSA operation. Formatting turns a random RSA result into a useful signature only when every required field is valid. section 9.6.1 section 9.7
A signature’s recovered cleartext follows this structure:
- Begin with the two bytes 00 01. section 9.6.1
- Fill the padding region entirely with FF bytes, then add a 00 separator. section 9.6.1 section 9.7
- Append an ASN.1 identifier for the hash algorithm and the computed hash digest. section 9.6.1
Why validation must be exact
With a small public exponent such as e = 3, an attacker can construct values whose cube resembles a desired cleartext. Weak checks that accept incorrect padding can therefore enable a forged signature; requiring every padding byte to equal FF blocks this failure. section 9.7
Figure 9.9 PKCS#1 v1.5 formatting for input to RSA signatures: The padding area should be filled with FF bytes.
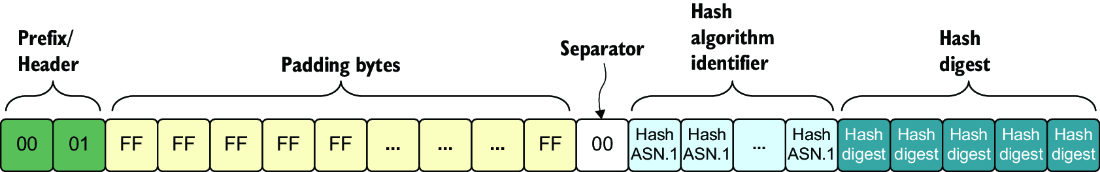
Inspect the byte-level signature layout, including the FF-filled padding area. section 9.6.1


