A security group is a cloud network control that works like an application-level firewall, permitting or restricting traffic by IP address and port. section 9.2
Use security groups as an additional boundary inside a VPC. For example, keep databases in private subnets and restrict inbound access to approved services rather than exposing them to the internet. section 9.2
Layered network access
An API gateway can expose tested public endpoints, while a bastion server provides controlled access to private APIs and databases. Security groups add IP- and port-based restrictions within this topology. section 9.2
Figure 9.10 The DMZ is a region of our network that is exposed to the internet. It’s good practice to channel inbound traffic through the DMZ and keep all our services in private subnets. The DMZ can include elements such as an API gateway and bastion server.
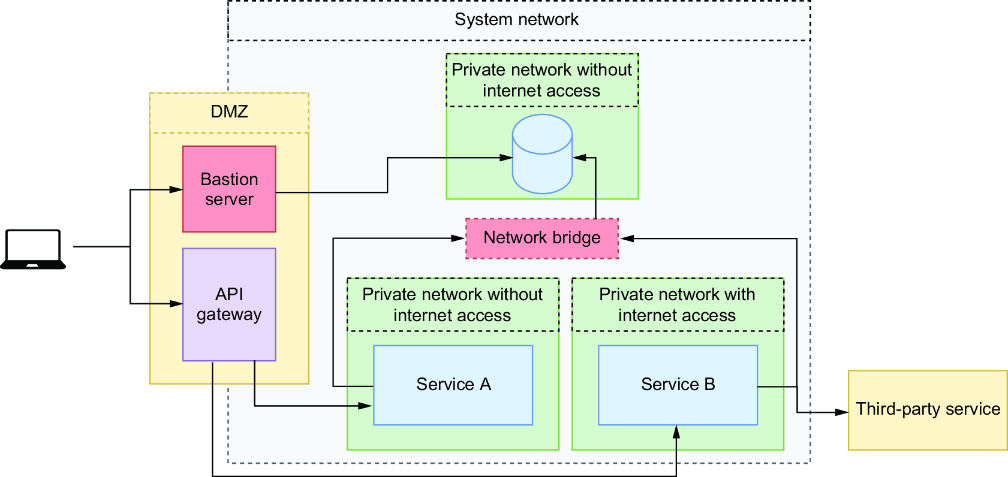
Use the network-topology diagram to see how a DMZ, API gateway, bastion server, and private subnets limit exposure. section 9.2


