Security incidents uncovered measures the number of incidents discovered through threat hunting and handed to the incident response team. Treat it as a time-bound performance metric, such as incidents uncovered during the past month, quarter, or year. Its value increases when paired with an identified audience, a clear representation, and a trend over time. section 12.3 section 2.7.1
Use the metric consistently by defining:
- The counting rule: include incidents uncovered by the threat-hunting process and referred to incident response. section 2.7.1
- The reporting period: specify a month, quarter, year, or another interval so results can be compared over time. section 12.3
- The presentation: report a number, identify the audience, and distinguish overall practice results from an individual play, process, or technology. section 12.3
Operations dashboard
A monthly dashboard reports eight threat-hunting expeditions and three incidents uncovered. A six-month view further breaks incidents down by severity, helping operations managers compare both volume and risk over time. section 12.5.3
Figure 12.7 Threat-hunting dashboard for the security operations manager
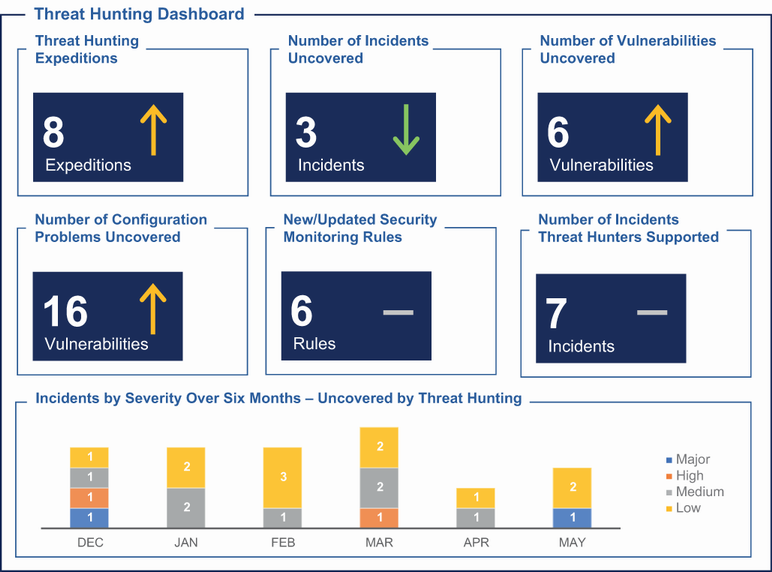
Use the threat-hunting dashboard to view incident discoveries alongside expeditions, vulnerabilities, configuration problems, monitoring rules, and severity trends. section 12.5.3
