A service account is a non-human identity that software or automated processes use to authenticate and access resources. Its permissions should match the application’s actual access path, including intermediary services such as database proxies. section 11.2.1 section 11.2.2
Use service-account configuration as an operational boundary for infrastructure management and troubleshooting:
- Extract project-level IAM service accounts and roles from a monolithic IaC configuration by copying the configuration, initializing separate state, importing existing resources, verifying an unchanged plan, and then removing the originals. section 10.2.1
- Check configuration drift before diagnosing a failure; compare the declared permissions with the active service-account policy, then investigate whether any difference affects functionality. section 11.2.1
- Trace dependencies between the service account and consuming resources, checking that expected relationships match production behavior. section 11.2.2
Database access through a proxy
The promotions server uses a service account with roles/cloudsql.admin. Although the application appears to connect to localhost, the Cloud SQL Auth proxy uses the service account to authenticate and access the database. The account therefore needs database permissions even when application code contains no database credentials. section 11.2.2 section 11.2.1
Figure 11.6 The promotions application accesses the database through a proxy, which needs a service account with database permissions.
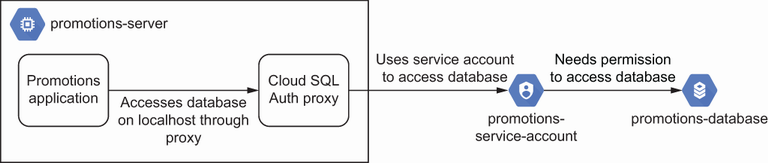
Shows how a proxy-mediated database connection makes the server’s service-account permissions necessary. section 11.2.2









