liveBook · Manning

Service principal

As explained in Terraform in Depth: Infrastructure as Code with Terraform and OpenTofu

A service principal is an identity representing an application or automated service for authentication and authorization.

A service principal is the cloud identity that an external identity provider maps to when an application or automated service needs authorization. With OpenID Connect, authentication establishes that a workflow or stack is genuine; mapping it to a service principal gives the cloud platform an identity whose permissions can be controlled. section 8.5.1

Mapping an automated workflow

A GitHub Actions workflow can present an OIDC identity to Azure, which maps that identity to a service principal. The relationship should be restricted to the intended repository and workflows; otherwise, other users of the identity provider may gain access. Vendor-specific subject fields and tokens determine how those restrictions are expressed. section 8.5.1

Figure 8.13 OIDC IdP to identity mapping
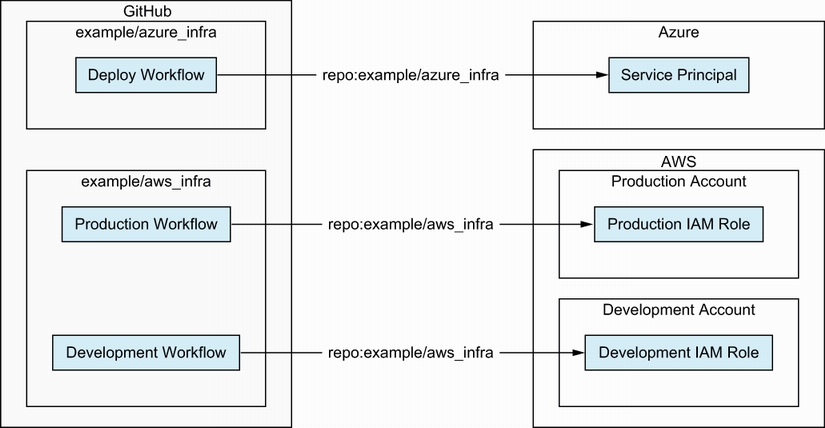
Trace the relationship from an OIDC identity provider to the cloud identity used for authorization. section 8.5.1


How Terraform in Depth: Infrastructure as Code with Terraform and OpenTofu covers it

How deep it goes
Explains the identity-mapping model and access restrictions, but defers concrete Azure configuration details.
Examples
Uses GitHub Actions and Spacelift identities mapped to cloud authorization identities, contrasting Azure service principals with AWS IAM roles.
What it assumes
Assumes familiarity with an external identity provider and authentication, while distinguishing authorization as the next step.
What you can do after
Evaluate how an automated identity becomes authorized and where repository, workflow, or stack restrictions must apply.
How it connects
Connects service principals with OpenID Connect, identity providers, authentication, authorization, and identity and access management.

Also explained in

Compare how 3 books explain service principal →

Related concepts

This explainer was generated by Manning's knowledge graph from the text of Terraform in Depth: Infrastructure as Code with Terraform and OpenTofu. The section links point to the parts of the book it draws on.
