A single VPC places Anthos resources in one GCP project and one flat network. It is the simplest topology for small environments and can also serve multiple teams sharing that project. section 10.1.1
Manage connectivity and assess the main trade-offs through these architectural controls:
- Control network-layer traffic with VPC firewall rules. section 10.1.1
- Restrict traffic inside Kubernetes with NetworkPolicies. section 10.1.1
- Apply service-level authentication and authorization through Anthos Service Mesh policies. section 10.1.1
- Simplify network administration because resources communicate across the flat network when security rules allow it. section 10.1.1
- Plan for growth because large implementations can encounter VPC limits and may require separate projects or more complex VPC designs. section 10.1.1
Small GCP project
A small Anthos environment contained in one GCP project can place all resources in one VPC, allowing teams and platform resources to communicate without additional network-connection configuration. section 10.1.1
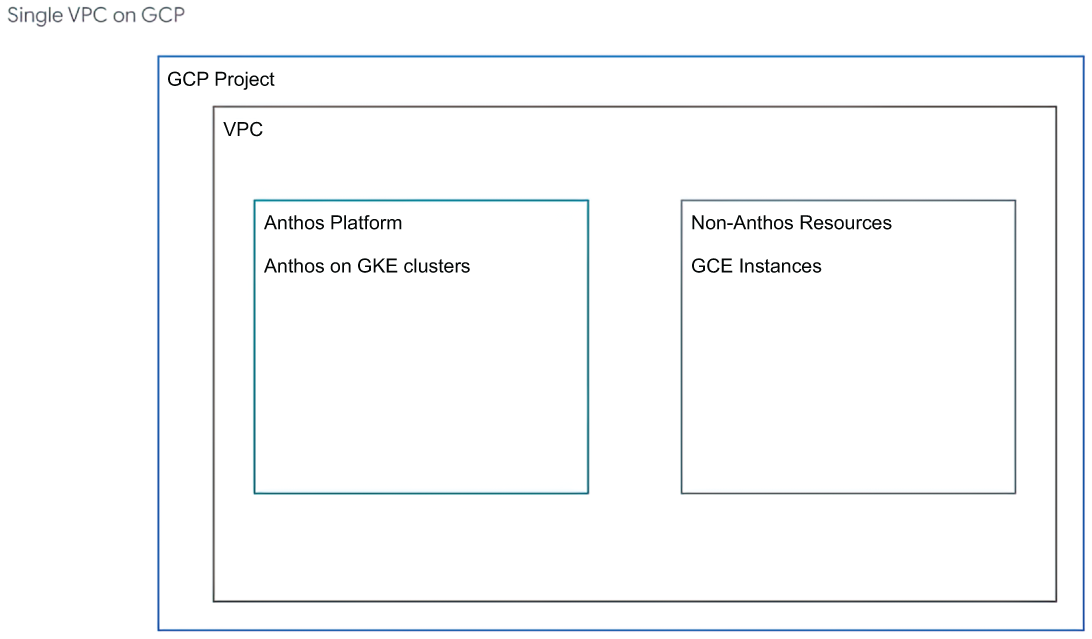
Use the architecture figure to inspect how a single VPC organizes resources within one flat GCP network. section 10.1.1
