STRIDE is a repeatable way to look for security threats while designing a system. Review the architecture before writing code, and use the framework whenever you examine a system diagram. section 11.6
Check the design against six threat categories:
- Spoofing: could someone impersonate a user or service? section 11.6
- Tampering: could someone modify data in transit or at rest? section 11.6
- Repudiation: could someone deny an action because it was not recorded? section 11.6
- Information disclosure, denial of service, and elevation of privilege. section 11.6
Spot the weak link
A rogue container might impersonate OrderService to send database commands. An attacker might alter an order’s shipping address, or an administrator might delete a table without leaving a record. STRIDE turns these into design questions to investigate before deployment. section 11.6
Figure 11.8 As the Risk Scout, Archie looks past the "Happy Path" to find the hidden cracks where an attacker might try to break the system.
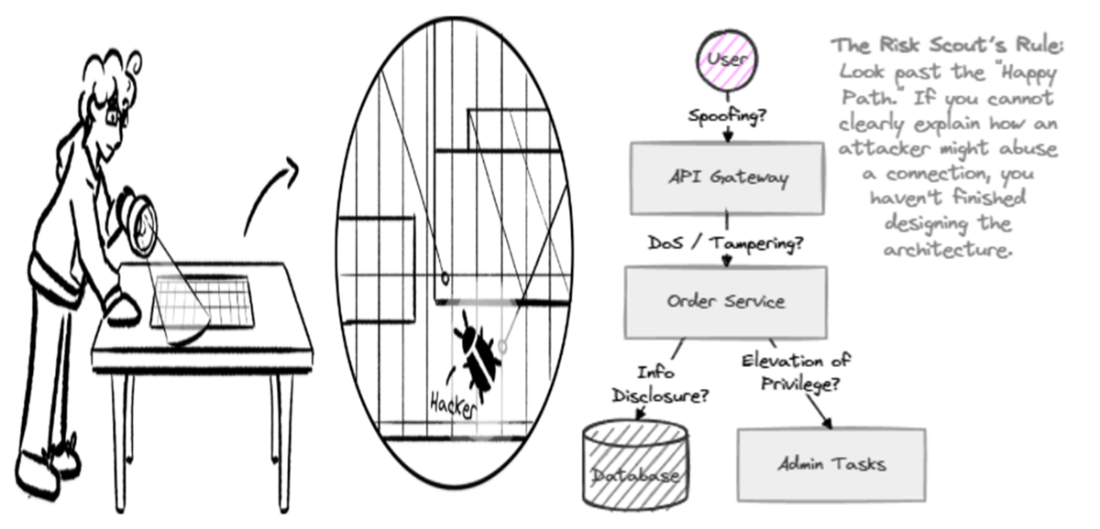
The risk-scout illustration emphasizes looking beyond the happy path for places an attacker could exploit. section 11.6

