Textbook RSA encrypts a message by treating its bytes as a number and raising that number to a public exponent modulo a public modulus. It is useful for understanding RSA, but unsafe when used directly. section 6.3.1 section 6.3.2
The basic operation follows a short sequence:
- Represent the message as an integer m. section 6.3.1
- Publish a public exponent e and modulus N; the simplified explanation first uses a prime p. section 6.3.1
- Compute ciphertext = m^e mod N. section 6.3.1
- Recover the message by exponentiating with the private exponent d modulo N. section 6.3.1
A tiny encryption example
With m = 2, e = 2, and p = 5, encryption gives 2^2 mod 5 = 4. Real RSA uses a public modulus N = p × q rather than the simplified prime-modulus example. section 6.3.1
The danger is determinism. An attacker can encrypt likely small messages, such as every number from 0 through 100, and compare the results with a target ciphertext. Matching ciphertexts reveal the plaintext. RSA ciphertexts are also malleable, so naive encryption does not provide a safe security boundary. section 6.3.2
Padding addresses the predictable-message problem by adding reversible random bytes before encryption. PKCS#1 v1.5 applied this idea, but Bleichenbacher's million-message attack showed that the standard could still permit adaptive chosen-ciphertext attacks, with mitigations repeatedly difficult to implement securely. section 6.3.2
Figure 6.12 RSA encryption works by exponentiating a number (our message) with the public exponent e modulo the public modulus N = p × q. RSA decryption works by exponentiating the encrypted number with the private exponent d modulo the public modulus N.
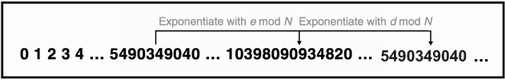
Diagram the public-exponent encryption and private-exponent decryption flow using the RSA modulus N = p × q. section 6.3.1

