USERADMIN is Snowflake’s system-defined administrative role for creating users and roles and managing the users and roles it creates. Its privileges cannot be revoked, and the role cannot be dropped. section 10.1.1
Use USERADMIN for role-definition tasks, while assigning other responsibilities to their designated roles:
- Create access roles and functional roles with CREATE ROLE. section 10.1.3
- Use SECURITYADMIN to grant object privileges and role memberships. section 10.1.1 section 10.1.3
- Use SYSADMIN to create warehouses, databases, and other account objects, then incorporate functional roles into the role hierarchy. section 10.1.1
Creating roles for a bakery environment
After preparing the database and schemas with SYSADMIN, switch to USERADMIN and create the access roles BAKERY_FULL and BAKERY_READ, followed by the functional roles DATA_ENGINEER and DATA_ANALYST. Switch to SECURITYADMIN afterward to grant privileges and role memberships. section 10.1.3
Figure 10.1 Role-based access control configuration of the environment used in the example in this chapter. The environment includes two functional roles, DATA_ENGINEER and DATA ANALYST, and two access roles, BAKERY_FULL and BAKERY_READ. Access roles are granted to functional roles, and functional roles are granted to the SYSADMIN role.
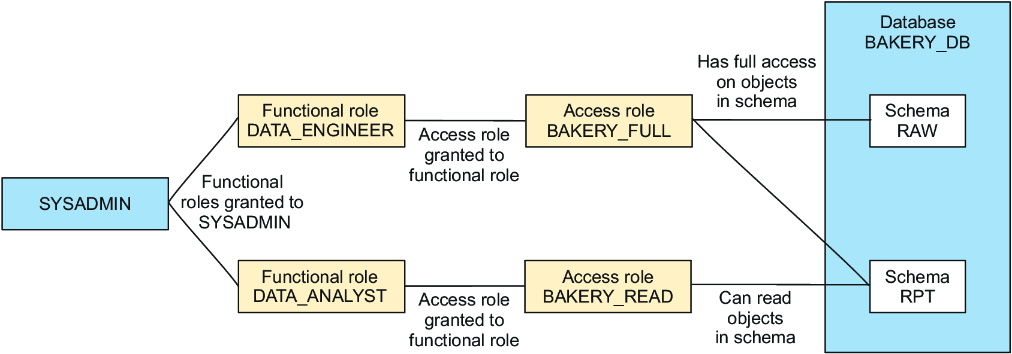
Role-based access control separates access roles from functional roles: USERADMIN creates the roles, SECURITYADMIN grants access, and SYSADMIN receives the functional-role hierarchy. section 10.1.3
