A virtual private cloud (VPC) is an isolated cloud network environment. In AWS, resources in separate VPCs cannot communicate by default, helping separate platform components and limit exposure. section 9.2
Use VPCs as part of network segmentation: connect VPCs only through necessary peering, place internet-facing components in a DMZ, and keep services in private subnets. Restrict traffic with subnet ACLs and security groups, which control permitted IP addresses and ports. section 9.2
API platform layout
Channel inbound traffic through an API gateway in the DMZ while keeping internal APIs and databases in private subnets. A hardened bastion server can provide controlled access to those private resources. section 9.2
Figure 9.10 The DMZ is a region of our network that is exposed to the internet. It’s good practice to channel inbound traffic through the DMZ and keep all our services in private subnets. The DMZ can include elements such as an API gateway and bastion server.
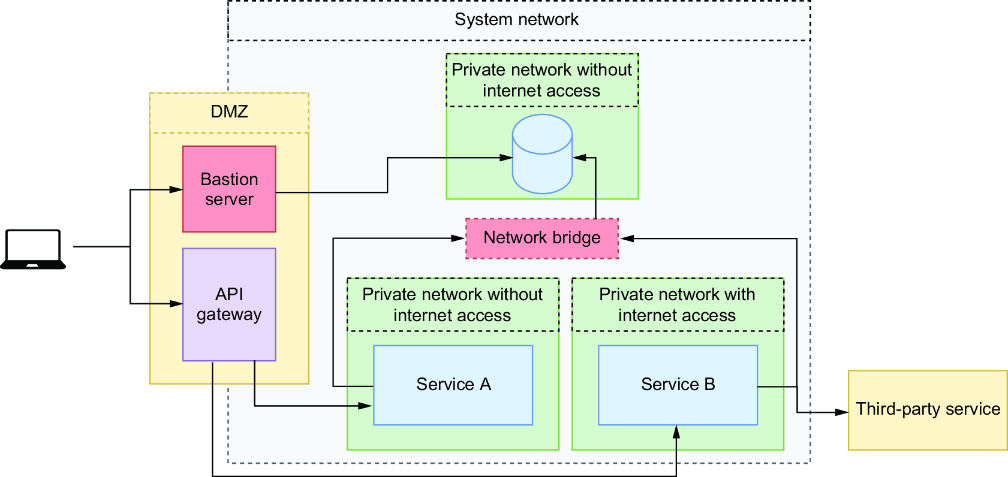
Use the network-topology figure to distinguish the internet-facing DMZ from private service subnets. section 9.2



