A witness is private data used by a prover to satisfy a proof statement without revealing the underlying secret. In a SNARK, public data is the statement and private data is the witness; the verifier receives only public information and the proof. section 19.2 section 19.7
Implementation-wise, the witness fills secret wires in a quadratic arithmetic program. Wire values feed multiplication gates and must satisfy the QAP equations; an invalid witness causes proof verification to fail. section 19.2 section 19.7
A witness participates in the proof flow as follows:
- The prover combines statement values, witness values, and a common reference string to create a proof. section 19.7
- Random values can be added so repeated records produce distinct proofs and do not leak information. section 19.7
- The verifier checks the proof against the statement without learning the witness. section 19.7 section 1.3.4
Medical-record witness
A QAP can use a medicine number, dose, and patient number as inputs. The patient number belongs to the private witness, while the proof establishes that some patient received the specified medicine at the known dose without identifying that patient. section 19.2
Figure 19.2 Example quadratic arithmetic program
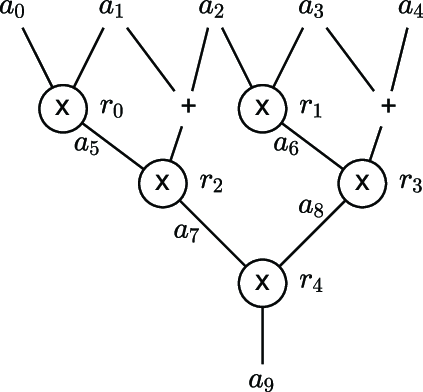
Use the quadratic arithmetic program diagram to trace how private wire values propagate through multiplication gates and contribute to the proof statement. section 19.2

