Microsoft Entra ID, formerly Azure Active Directory (Azure AD), is Azure’s cloud-based identity and access management (IAM) service. It helps give the right users access to the right resources at the right time and for the right reasons through authentication, authorization, custom roles, and identity governance. section 2.0 section 2.1.1
An Azure tenant represents an organization and contains a dedicated directory for users, groups, applications, and IAM functions. A tenant can contain many Azure subscriptions; each subscription is associated with one Entra ID directory, allowing identities to be used across those subscriptions. section 2.1.1
Use Entra ID as part of layered identity security:
- Detect suspicious sign-ins and require multifactor authentication (MFA) to resist brute-force attempts. section 1.8.1
- Protect privileged identities by requiring additional controls, such as a password change, when identity protection detects possible compromise. section 1.8.1
- Treat identity protection as one control in a broader defense: compromised identities can enable lateral movement and phishing activity. section 1.8.1
Password plus MFA
A user authenticates to Azure by presenting a username and password to Entra ID. Because anyone holding those credentials could attempt the same sign-in, MFA adds another protection when credentials are disclosed. section 2.2.1
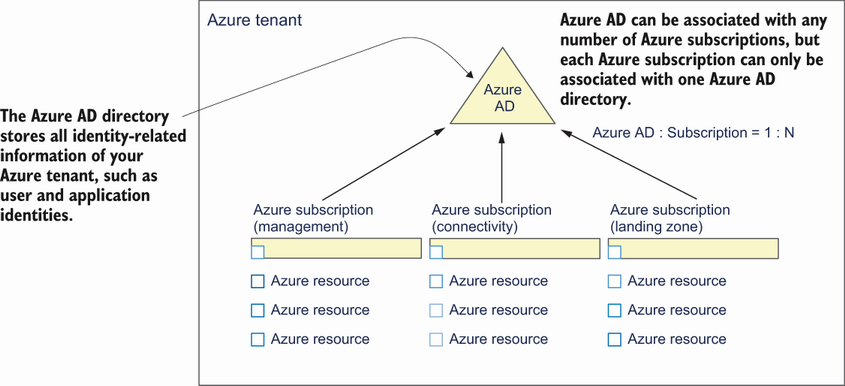
View the tenant-to-subscription relationship: one tenant directory can serve multiple subscriptions, while each subscription has one associated directory. section 2.1.1


