Azure Policy keeps cloud resources aligned with organizational rules. It evaluates choices such as VM images, regions, storage, backups, and auditing, then reports or helps enforce compliance. section 3.5.3 section 6.1
Common policy decisions include:
- Allow only approved images when creating virtual machines. section 3.5.3
- Require managed disks instead of custom virtual hard drives. section 3.5.3
- Restrict resource creation to approved Azure regions. section 3.5.3
- Use built-in policies or define custom policies with JSON syntax. section 3.5.3
A noncompliant VM
A newly created VM can receive an implicit policy assignment and appear as noncompliant. Investigate the reason, then change the VM or establish procedures that prevent the same violation on future deployments. section 3.5.3
Azure Policy works alongside other safeguards: RBAC controls access, while Microsoft Defender for Cloud surfaces security recommendations and vulnerabilities. Policy is the rulebook; the surrounding tools help protect and monitor the environment. section 6.1
Figure 3.31 The single policy assigned to the new ActionVM
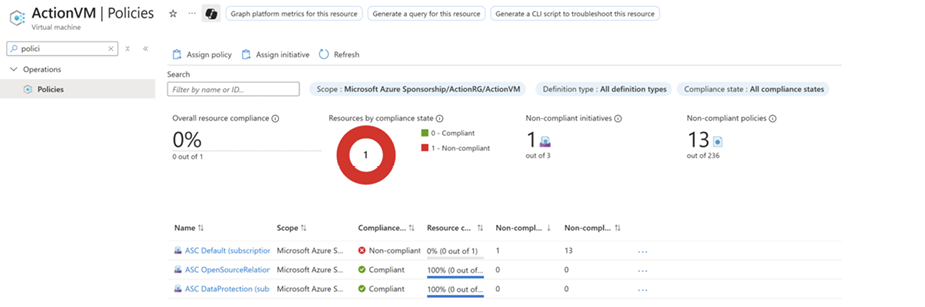
Inspect the policy assigned to the example VM and use its compliance status as a starting point for investigation. section 3.5.3

