Base64 encodes arbitrary data using a fixed 64-symbol alphabet. It makes binary or credential strings convenient to transfer, but provides neither encryption nor confidentiality. section 2.1 section 2.2
Use Base64 with these practical constraints:
- Encode the string username:password when constructing an HTTP Basic Authorization header. section 2.1
- Prefix the encoded value with Basic in the Authorization header. section 2.2
- Protect credentials with HTTPS because intercepted Base64 data remains readable. section 2.2
- Recognize Base64-encoded JWT header and body data as readable content rather than encrypted secrets. section 13.2.2
Constructing an HTTP Basic header
Encode user:password with a Base64 tool, then send Authorization: Basic followed by the result. The resulting request authenticates like curl -u user:password, provided the credentials are valid. section 2.1
Figure 2.1 Our initial application employs HTTP Basic for user authentication and authorization when accessing an endpoint. It offers a REST endpoint at a specified route (/hello). Upon a successful request, it issues an HTTP 200 status message along with a response body. This instance illustrates the default authentication and authorization mechanisms set up by Spring Security.
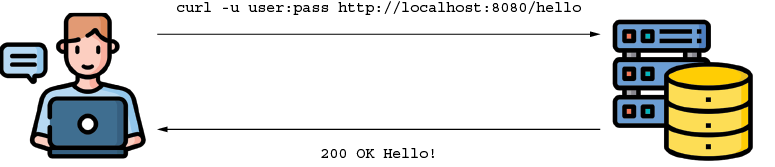
Trace how a Spring endpoint receives HTTP Basic credentials and returns a successful response after authentication. section 2.1






