liveBook · Manning

Conmon

As explained in Podman in Action: Secure, rootless containers for Kubernetes, microservices, and more

conmon is a lightweight C program that monitors a container, manages attached I/O streams, and reports the container's exit status.

conmon is a lightweight C container monitor. It launches the configured OCI runtime, remains after Podman exits, monitors the container, reports its exit status, and manages interaction with its standard streams. section 4.1 section 6.2.4

conmon connects Podman’s control flow with the running container by:

  • Passing the OCI specification and rootfs path to crun or runc. section 4.1
  • Providing a socket for attach operations and monitoring STDIN, STDOUT, and STDERR. section 6.2.5
  • Writing STDOUT and STDERR to logs and reporting the container’s exit code to Podman. section 4.1
  • Running cleanup after the container exits, including in rootless workflows. section 6.2.4

Detached container

podman run -d -p 8080:8080 --name myapp registry.access.redhat.com/ubi8/httpd-24 leaves Podman detached while conmon continues monitoring the container; podman attach reconnects through conmon. section 6.2.5
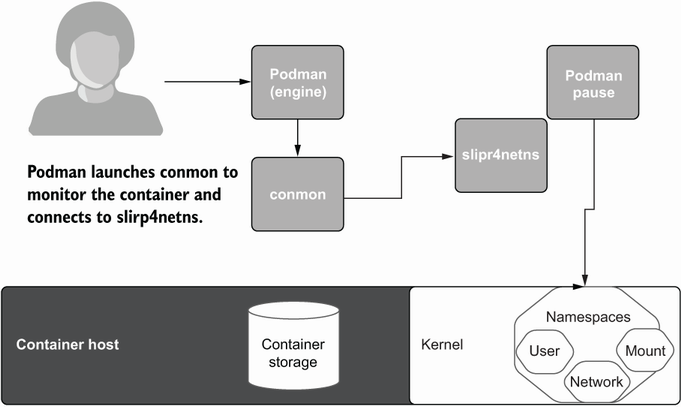
Figure 6.7 Podman launches the container monitor, which launches the OCI runtime.

The launch diagram shows Podman starting conmon, which then starts the OCI runtime. section 6.2.4

How Podman in Action: Secure, rootless containers for Kubernetes, microservices, and more covers it

How deep it goes
Explains process handoff, stream sockets, logging, exit reporting, and cleanup, but defers OCI runtime internals.
Examples
Uses Podman pods, infra containers, detached HTTP servers, attach sockets, and OCI-runtime launch diagrams.
What it assumes
Assumes basic Podman and container knowledge while introducing conmon’s role in rootless container startup.
What you can do after
Operate detached containers and reconnect to their streams with Podman attach while understanding conmon’s lifecycle role.
How it connects
Connects Podman with OCI runtimes, rootless containers, Linux namespaces, cgroups, and slirp4netns.

Related concepts

This explainer was generated by Manning's knowledge graph from the text of Podman in Action: Secure, rootless containers for Kubernetes, microservices, and more. The section links point to the parts of the book it draws on.