Session-cookie authentication keeps authentication state in a server-side session and gives the client a unique sessionId in a cookie. section 9.1.2
The request flow works as follows:
- Store the user’s authentication information in a key/value service on the web server or an external server or cluster. section 9.1.2
- Assign the stored session an autogenerated unique sessionId. section 9.1.2
- Send the sessionId to the browser in a cookie. section 9.1.2
- Resend the cookie on later requests so the server can retrieve the session and perform authorization checks. section 9.1.2
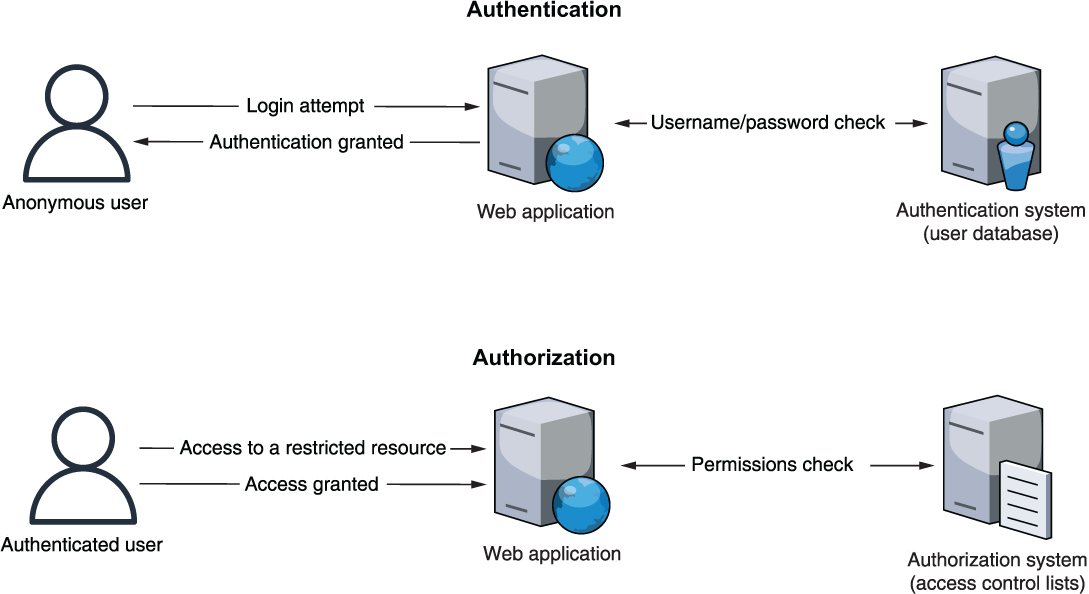
Use the authentication and authorization flow diagram to trace how login state persists across requests. section 9.1.2









