liveBook · Manning

Defender profile

As explained in Azure Security

The Defender profile is a Microsoft-developed Kubernetes agent deployed on cluster nodes to collect security signals for Microsoft Defender for Containers.

The Defender profile is a Microsoft-developed native Kubernetes agent deployed on every cluster node. It collects node security signals and sends them to Microsoft Defender for Cloud for analysis, enabling runtime threat detection such as crypto-mining activity. section 7.2.2

Use the profile to strengthen Kubernetes runtime monitoring:

  • Deploy it automatically to cluster nodes through auto-provisioning. section 7.2.2
  • Combine node-level signals with control-plane Kubernetes audit logs and security events for layered threat detection. section 7.2.2
Figure 7.4 An architecture diagram of Defender for Containers for an Azure Kubernetes Service cluster
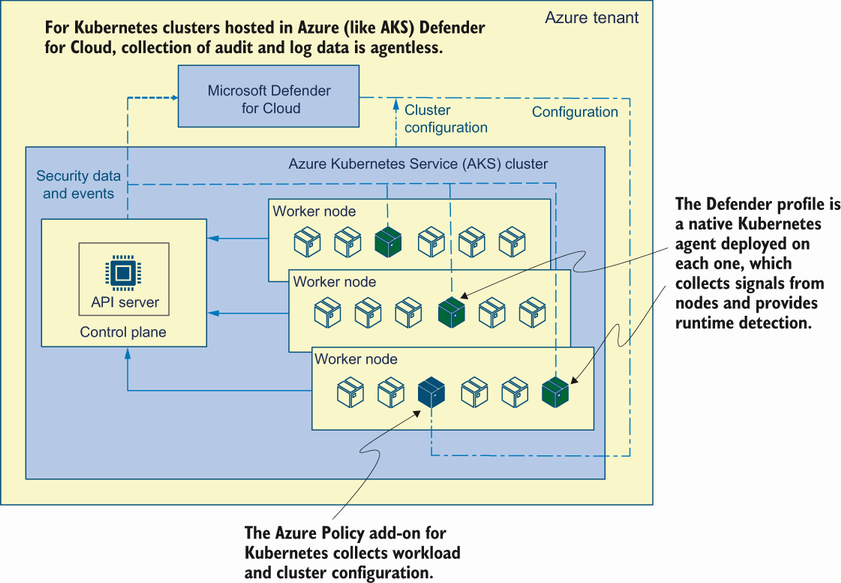
Architecture diagram showing how Defender for Containers uses the Defender profile with an Azure Kubernetes Service cluster. section 7.2.2

How Azure Security covers it

How deep it goes
Explains the agent’s deployment, signal collection, analysis destination, and relationship to control-plane monitoring.
Examples
Uses crypto-mining activity on cluster nodes as an example of suspicious behavior the profile can help detect.
What it assumes
Assumes a Kubernetes cluster with control-plane and worker-node components requiring security monitoring.
What you can do after
Operate/configure automatic deployment of a node agent for continuous Kubernetes runtime threat detection.
How it connects
Connects Kubernetes nodes with Microsoft Defender for Containers, Microsoft Defender for Cloud, control-plane audit logs, and auto-provisioning.

Related concepts

This explainer was generated by Manning's knowledge graph from the text of Azure Security. The section links point to the parts of the book it draws on.