Gatekeeper is an open-source Kubernetes admission controller that integrates with Open Policy Agent (OPA) and Rego to enforce policy at deployment time. section 4.1.1
Use it to accept or deny Kubernetes deployments based on required configuration, such as labels needed by cost-optimization and tracking systems. Security teams can own reusable pipeline code and policies while teams receive immediate verification at the point of change. section 4.1.1
Gatekeeper structures policies more like Kubernetes resources than general OPA policies. That specialization is useful for Kubernetes compliance but can create friction when organizations seek one shared policy-as-code standard across disciplines. section 4.1.1
Figure 4.4 Admission controller built using Gatekeeper (https://github.com/open-policy-agent/gatekeeper), which checks for labels on the deployment
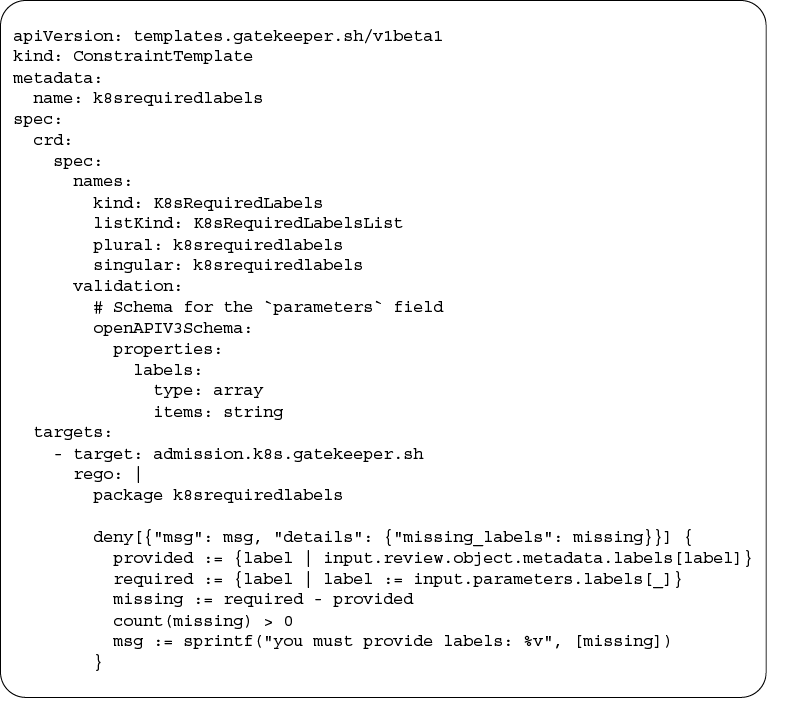
See an admission controller built with Gatekeeper that checks whether deployments contain required labels. section 4.1.1

