Gatekeeper is a Kubernetes admission-control policy engine. It evaluates API requests against configured policies so a cluster can reject resources that violate security or operational requirements. Anthos Configuration Management (ACM) includes Gatekeeper through Policy Controller; organizations can also deploy the open-source release and take responsibility for its support. section 13.4.1 section 13.3
With Policy Controller enabled, a ValidatingWebhook configuration registers the engine with the Kubernetes API server. For a Pod creation request, the API server sends the request to the Gatekeeper service, which passes it to a Gatekeeper Pod for policy evaluation. A denial prevents the object from being created and returns the policy error through the API server. Gatekeeper uses constraint templates and constraints to express those decisions. section 13.4.1
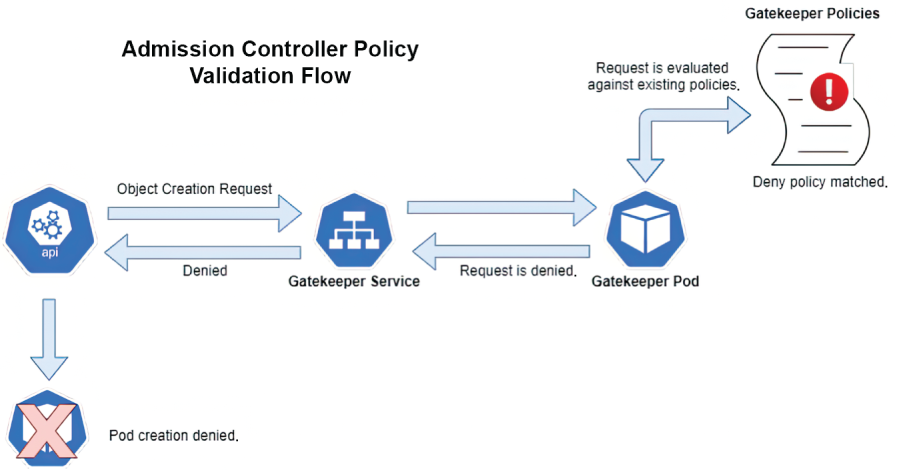
Follow the request from the API server through policy evaluation and back to an allow-or-deny result. section 13.4.1
A practical policy target is a container configured to run as root with privileged access: together, those settings can let it access the host and change or extract data. Other sensitive manifest fields include hostPID, hostIPC, hostNetwork, and allowPrivilegeEscalation. Policies can also address disruption risks such as unapproved images, conflicting Ingress URLs, and workloads that consume excessive node resources. section 13.4
Test a privileged-container constraint
A K8sPSPPrivilegedContainer constraint can match Pods. Set enforcementAction to dryrun to inspect reported violations before enforcing it; the illustrated results include privileged system Pods. Account for such existing workloads before deciding where a denial should apply. section 13.4.1
Scope matters. Gatekeeper configuration can exempt namespaces from audit, webhook admission, resource sync, or all three; these choices have different effects. A configuration example excludes kube-system and gatekeeper-system from every process. Treat broad exemptions carefully, because a webhook exemption removes admission checks even though audit and sync can continue. section 13.4.1
Policy evaluation averages about one millisecond in the described deployment, but a poorly performing custom policy can add cluster-wide request latency. An admission-controller problem can obstruct every deployment request, making support arrangements operationally important. Gatekeeper policies are also an option when migrating away from deprecated PodSecurityPolicies; supplied policy libraries cover common concerns, while custom policies can be written in Rego. section 13.4.1 section 13.3
For a PodSecurityPolicy migration, Gatekeeper provides a repository of replacement policies. Select and test constraints against the cluster’s existing workloads rather than assuming a replacement policy can be enforced unchanged. section 13.4.3 section 13.4.1

