Identity and access management administers user accounts, identity, authentication, authorization, and permissions across distributed application services. Implementing these concerns early clarifies who can do what and when. section 2.4 section 2.4.6
A frontend-facing service commonly handles the login flow through an OAuth2-compatible identity management service. That service validates credentials through an identity provider and supplies roles or group memberships; the frontend then propagates the authorization context to backend services. section 2.4.6
Distributed applications use identity management to:
- Protect operations from unauthorized actions, such as deleting conference presentations without organizer permissions. section 2.4.6
- Keep external users behind a frontend barrier instead of exposing every internal service directly. section 2.4.6
- Support social login through providers such as Google or GitHub without requiring separate application accounts. section 2.4.6
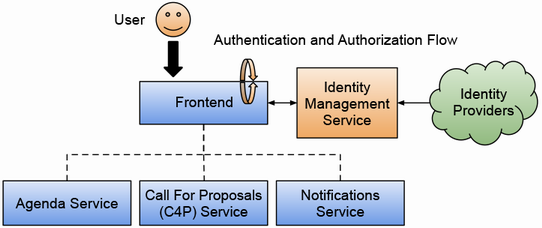
Trace how roles or group memberships move from the identity management service through the frontend to backend services. section 2.4.6



