Infrastructure as Code defines and manages computing infrastructure through machine-readable configuration instead of manual procedures. It supports DevOps and SRE by making infrastructure changes repeatable, reviewable, and automatable, while improving agility and reliability at scale. section 5.0 section 15.1.3
Its operational model combines:
- Declarative configuration describing the target state of a computing environment. section 5.2.2
- Provider mappings that translate configuration into cloud provisioning APIs. section 5.2.2
- Repository workflows such as commit, push, pull, merging, and branching for infrastructure and configuration files. section 15.1.3
- Automation, monitoring, and security practices that support continuous delivery and reliable operations. section 5.0
Provisioning GKE on AWS
Terraform can generate the AWS infrastructure for GKE on AWS, including load balancers, EC2 virtual machines, management services, and node pools. Administrators can initialize and apply the management service, retrieve credentials, and describe clusters or node pools with declarative configuration. section 5.2.2
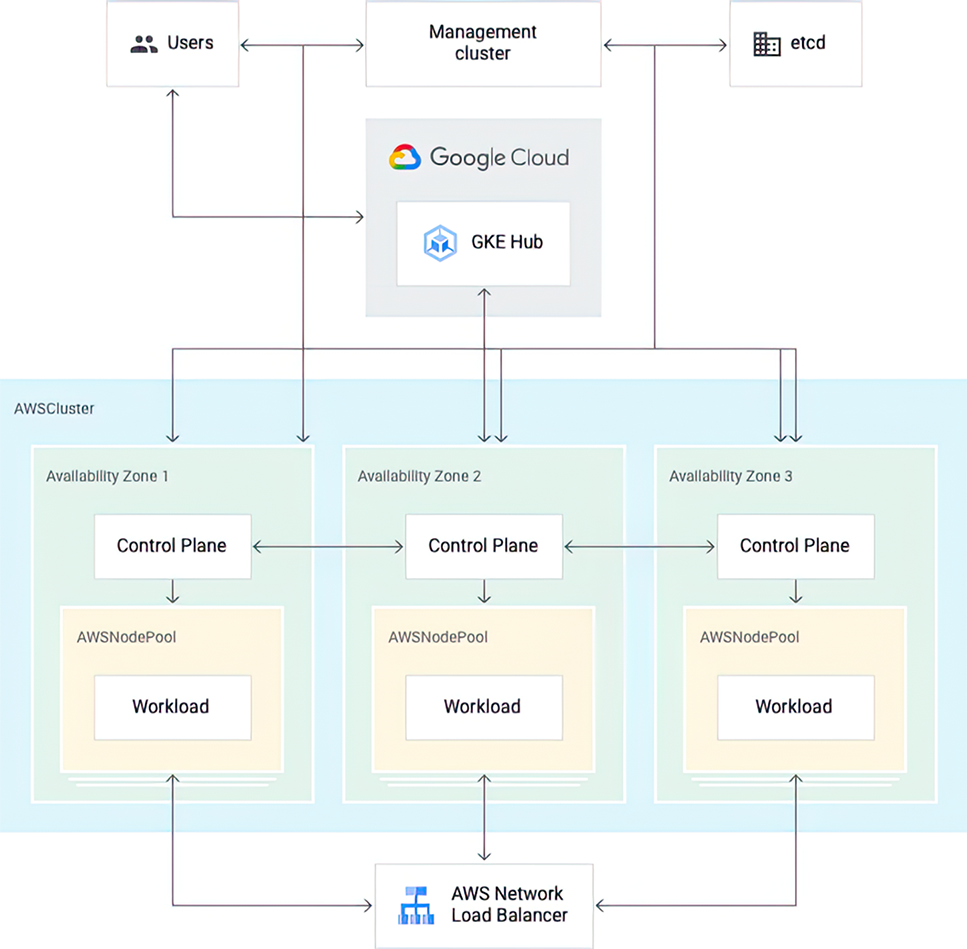
Use the architecture diagram to relate Terraform-managed AWS components to the GKE on AWS management service and cluster. section 5.2.2













