Automated log analysis is the computational examination of recorded system events to detect anomalies, policy-rule problems, and unexpected behavior. In authorization governance, it supports monitoring as policies move through creation, approval, deployment, use, and retirement. section 14.2 section 14.2
Governance toolkit
ACME places automated log analysis alongside architectural decision records, version control, CI/CD pipelines, and A/B testing for policy changes. Together, these tools support a policy life cycle that remains auditable, adaptable, and aligned with organizational intent. section 14.2 section 14.2
Figure 14.2 The policy management life cycle. Policies go through distinct stages (creation, review and approval, deployment and use, monitoring, and eventually retirement) with updates feeding back into the review process. The life cycle ensures that authorization policies remain current, coherent, and aligned with organizational intent.
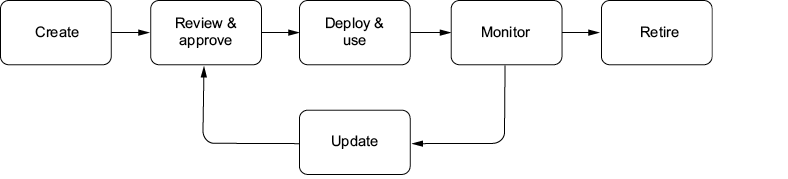
Use the policy life-cycle figure to locate log analysis within monitoring and connect operational findings to policy review and updates. section 14.2
