Code-to-cloud contextualization connects DevOps repository findings with cloud security posture management so teams can prioritize misconfigurations according to the resources and business effects they may affect. section 11.4 section 11.4.9
The approach enables security teams to:
- View repository vulnerabilities, secrets, and misconfigurations inside the Defender for Cloud dashboard. section 11.4
- Use Cloud Security Explorer to relate repositories and cloud resources through graph-based queries. section 11.4.9
- Determine which resources are exploitable and assess the resulting business effect. section 11.4.9
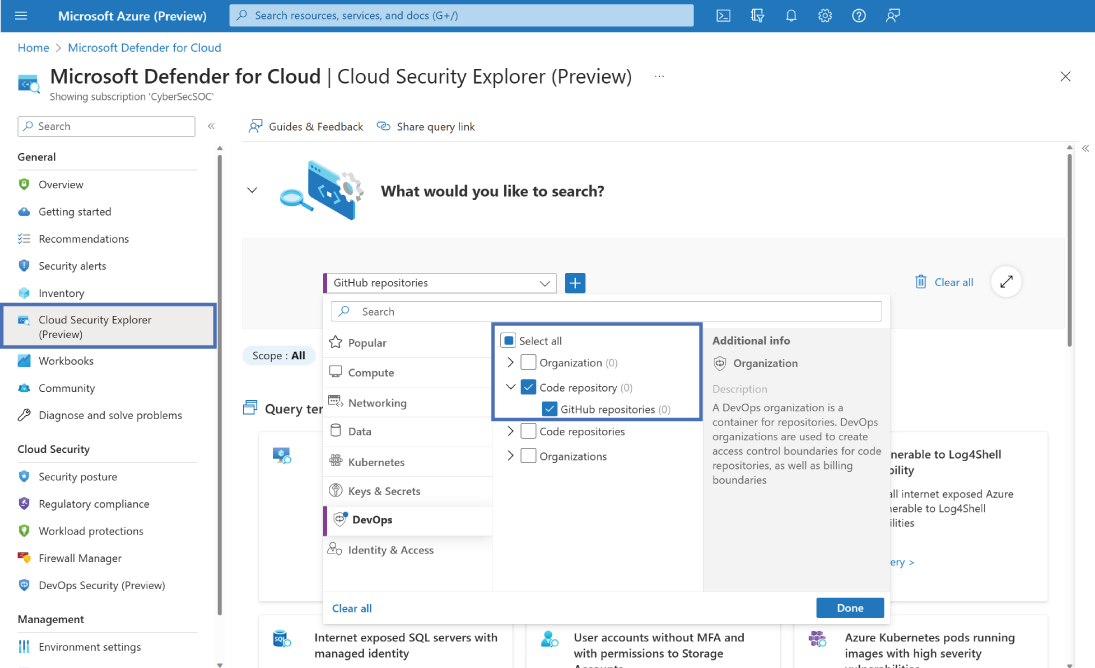
Use the integration diagram to trace how Defender for DevOps findings become queryable in Cloud Security Explorer. section 11.4.9
Internet-accessible repositories
Onboard repositories to Defender for DevOps, then write a Cloud Security Explorer graph query to determine whether any repositories are accessible to the internet. section 11.4.9
