Organization level is a shared configuration scope for repositories in a GitHub organization. It centralizes policies and resources that should be available—or restricted—across more than one repository, while still allowing repository and environment settings to override organization-level secrets and variables with the same key. section 3.7
Use this scope to control self-hosted runner creation across the organization. Creation can be allowed for every repository, disabled for every repository, or enabled only for selected repositories. This limits where runners can be installed and helps keep unmanaged runner infrastructure from spreading. section 6.4
Organization-level settings support shared configuration with targeted access:
- Create organization secrets and variables for all repositories, private repositories, or a selected repository set. section 3.7
- Override an organization secret or variable at repository or environment level when a lower scope needs a different value. section 3.7
- Create runner groups only at organization or enterprise level, then expose each group to all or selected repositories. section 7.1
- Keep costly or specialized runners, such as GPU-enabled runners, away from repositories that only need ordinary jobs. section 7.1
- Treat public-repository access to self-hosted runners as a security decision; it is disabled by default for runner groups. section 7.1
Restricting a GPU runner group
Create an organization runner group with selected visibility and assign repository IDs that need GPU jobs. The REST API configuration can also restrict the group to named workflow files, preventing unrelated workflows from consuming the specialized runners. section 7.1
Disabling new self-hosted runner creation does not remove runners that already exist. Review affected organizations and remove existing runners manually when they no longer comply with the policy. Users may still create runners for repositories in their own personal namespace. section 6.4
Figure 3.11 The hierarchy for configuration variables and secrets
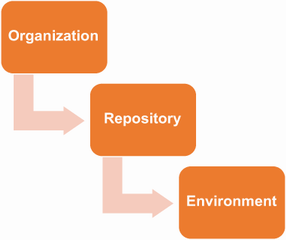
Use the hierarchy diagram to determine when an organization secret or variable is inherited and when a repository or environment value replaces it. section 3.7
