A policy is a declarative rule that specifies required behavior, configuration, or access conditions for managed resources. In Kubernetes and Anthos environments, policies regulate workload access, service-mesh traffic, cluster configuration, and security-sensitive resource settings. section 4.3.3 section 13.7
Use policies to establish controls at several operational boundaries:
- Restrict traffic between workloads or between users and workloads by request identity, protocol, and custom Istio attributes. section 4.3.3
- Enforce secure service-to-service communication with mTLS, including workload identity, encryption, and automated key and certificate rotation. section 4.3.3 section 13.7
- Prevent dangerous Kubernetes configurations, such as privileged containers or host namespace sharing, through Gatekeeper policy controls. section 13.4
- Apply infrastructure and security requirements consistently across managed clusters, using selectors when a policy should target only part of the fleet. section 13.7
Restricting service-mesh access
An operator can define an Istio authorization policy that allows or denies requests according to workload identity, protocol, and other Istio attributes. Each Envoy proxy evaluates authorization locally, so traffic is controlled at the workload boundary for HTTP, HTTPS, HTTP2, gRPC, and TCP services. section 4.3.3
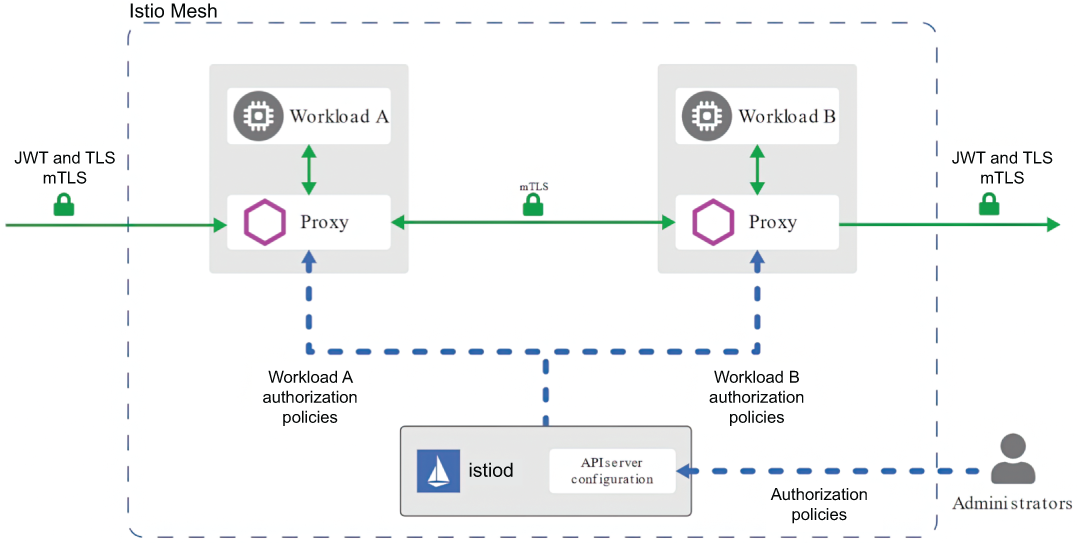
Use the architecture figure to trace how Istio authorization policies relate to the service mesh, namespaces, workloads, and Envoy enforcement points. section 4.3.3












