A random seed is the initial value used to initialize a pseudorandom number generator (PRNG) or cryptographically secure PRNG (CSPRNG). The generator deterministically derives its state and output sequence from that seed: using the same seed with a comparable generator produces the same sequence. This repeatability is useful for implementation tests, but it is fatal when unpredictability is required. section 2.2 section 2.2.2
Figure 2.7 TRNGs are used to seed PRNGs.
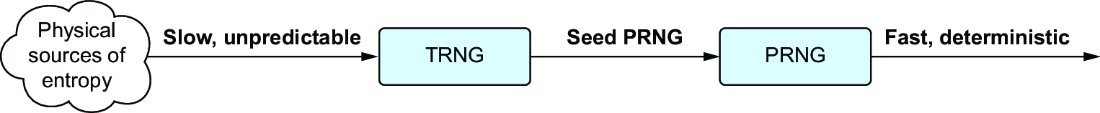
A TRNG supplies unpredictable seed material, while a faster PRNG expands that initial input into many values. section 2.2 section 2.2.2
A seed is not merely configuration; it is the root of a generator’s security. If an attacker knows a PRNG or CSPRNG seed, the resulting sequence can be reproduced, defeating randomness regardless of the later algorithm. For cryptographic use, seed CSPRNGs with high-quality values from a true random number generator (TRNG), whose inputs come from nondeterministic physical phenomena. section 2.2 section 2.3
Fixed seed for a reference sequence
An LCG compatible with C++ `minstd_rand` is seeded with `42` and emits ten expected values. A matching implementation can use that fixed sequence as a test oracle. The same hard-coded seed would be dangerous in a real PRNG deployment because anyone can reproduce its output. section 2.2.2
In a linear congruential generator, the seed is the initial value X₀. Each later state is calculated as Xₙ₊₁ = (aXₙ + c) mod m, so the seed starts the entire chain. LCGs expose an especially dangerous design: their output is their state. Observed outputs can let an attacker recover generator parameters, clone the generator, and predict subsequent values even when the original seed was not directly known. section 2.2.2 section 2.2.3
For cryptographic randomness, handle seeds defensively:
- Seed CSPRNGs from a TRNG rather than hard-coded, guessable, or weak default values. section 2.2 section 2.3
- Use a CSPRNG instead of a weak PRNG for cryptographic applications. section 2.3
- Periodically reseed a CSPRNG so one seed does not remain in use indefinitely; this helps protect against state-extension attacks. section 2.3
- Treat generator outputs and internal state design as security-relevant: a weak state-to-output relationship can enable prediction. section 2.2.3 section 2.3


