A resource owner is the person or entity that owns a protected resource and can authorize an application to access it. In OAuth 2.0, the owner delegates access without sharing account credentials with the application. section 23.3.2 section 23.4
The resource owner participates in the OAuth 2.0 authorization sequence:
- The client requests authorization to access the owner’s protected resource. section 23.3.2
- The owner logs in and grants permission to the client. section 23.3.2
- The client exchanges the authorization grant for an access token through the authorization server. section 23.3.2
- The client uses the access token to request the protected resource from the resource server. section 23.3.2
Google Calendar integration
A person who owns a Google account and its calendar is the resource owner. A scheduling application requests permission, receives delegated access through an access token, and then reads or manages calendar data within the approved scope. section 23.3.2
Figure 23.7 The basic OAuth 2.0 process. Through access delegation, the client application is able to access the resource owner’s protected resources on behalf of the owner.
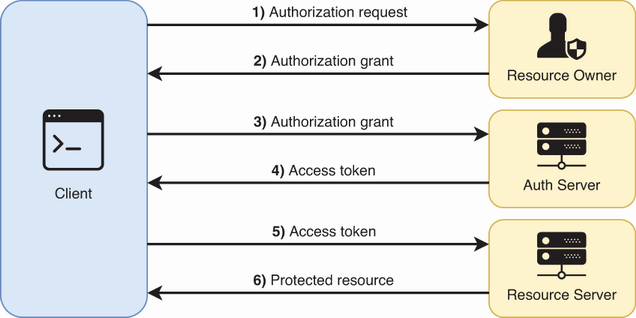
Use the OAuth 2.0 process diagram to distinguish the resource owner from the client, authorization server, and resource server. section 23.3.2

