The AWS account root user is the identity created with an AWS account. It has unrestricted access to every resource in that account, including EC2 instances, CloudFormation stacks, and IAM users. section 5.3 section 1.8
Treat the root user as an account-protection concern:
- Choose a strong password during account creation; a password of at least 20 characters is recommended. section 1.8.1
- Avoid using the root user for routine console or CLI work; create IAM users with permissions restricted to their roles. section 4.2.2 section 5.3
- Enable multifactor authentication for the root user to add protection beyond the password. section 5.3
- Protect access keys and passwords because stolen credentials can enable administrator-level access, data theft, resource usage, or deletion. section 4.2.2 section 5.3
Create a safer CLI identity
Open IAM in the AWS Management Console, create a user such as mycli with programmatic access, attach the required policy, and run aws configure with its access key, secret access key, region, and JSON output settings instead of using the root identity. section 4.2.2
Figure 5.4 An AWS account contains all the AWS resources and comes with an AWS account root user by default.
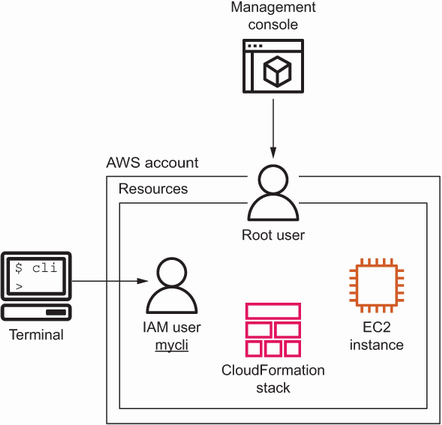
Use the account diagram to relate the root user to the AWS account and the resources contained within it. section 5.3


