A sector-specific law governs how organizations store, access, and use data within an industry whose information creates particular risks for individuals. section 8.2.1
Common examples include:
- HIPAA regulates protected health information handled by healthcare providers and insurers, often requiring explicit consent for sharing, access, or use. section 8.2.1
- FERPA gives students and parents rights to access and correct education records while restricting disclosure of personally identifiable information without consent. section 8.2.1
- GLBA requires financial institutions to explain data-sharing practices and provide customers with an opportunity to opt out. section 8.2.1
Analytics under sector-specific constraints
A business analytics team can work with data engineering to capture anonymized, aggregated snapshots in dedicated warehouse tables for organizational dashboards, reducing exposure of sensitive information while supporting metric tracking. section 8.2.1
Figure 8.3 Many types of sensitive information are governed by sector-specific laws, both in the US, as in the examples shown here, and around the world.
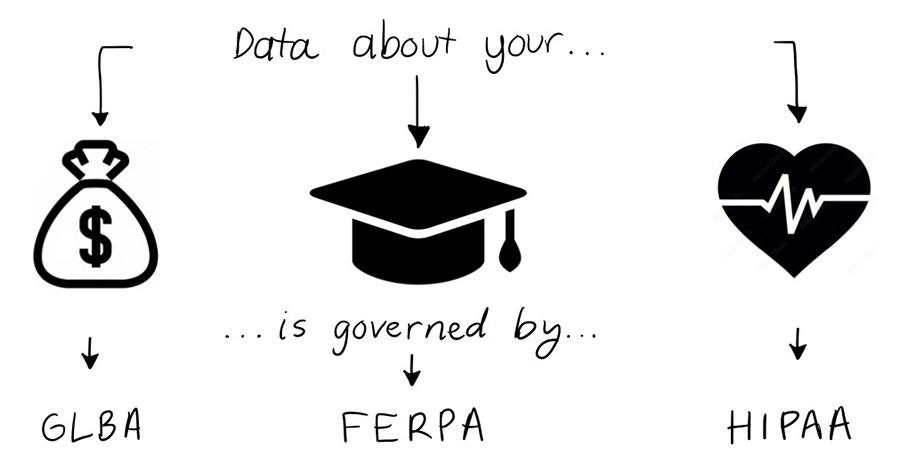
Compare how sector-specific laws govern sensitive health, education, and financial information in the United States and elsewhere. section 8.2.1

