SQL injection occurs when a web application puts crafted user input directly into a database query without proper validation or sanitization. The database may then execute the attacker’s instructions along with the intended query. section 12.3.2
A crafted login input
A normal query might look for a user named Alice: SELECT * FROM users WHERE username = 'Alice'. Replacing the username with ' OR 1=1 -- can make the condition always true, potentially returning every user row in the browser. section 12.3.2
Exposed database rows can put information at risk. SQL injection is one of several scripting attacks that exploit application weaknesses to gain unauthorized access or manipulate data. section 12.11 section 12.3.2
Figure 12.3 Illustration of an SQL Injection (SQLi) attack.
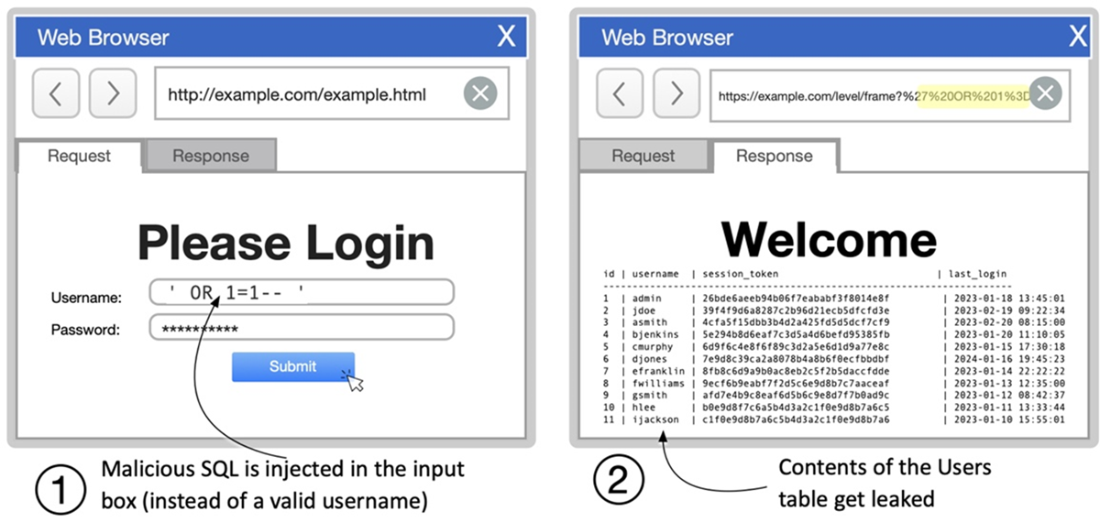
Illustrates how crafted input can affect a database query. section 12.3.2











